1. When an Ordinary Door Becomes a Security Risk
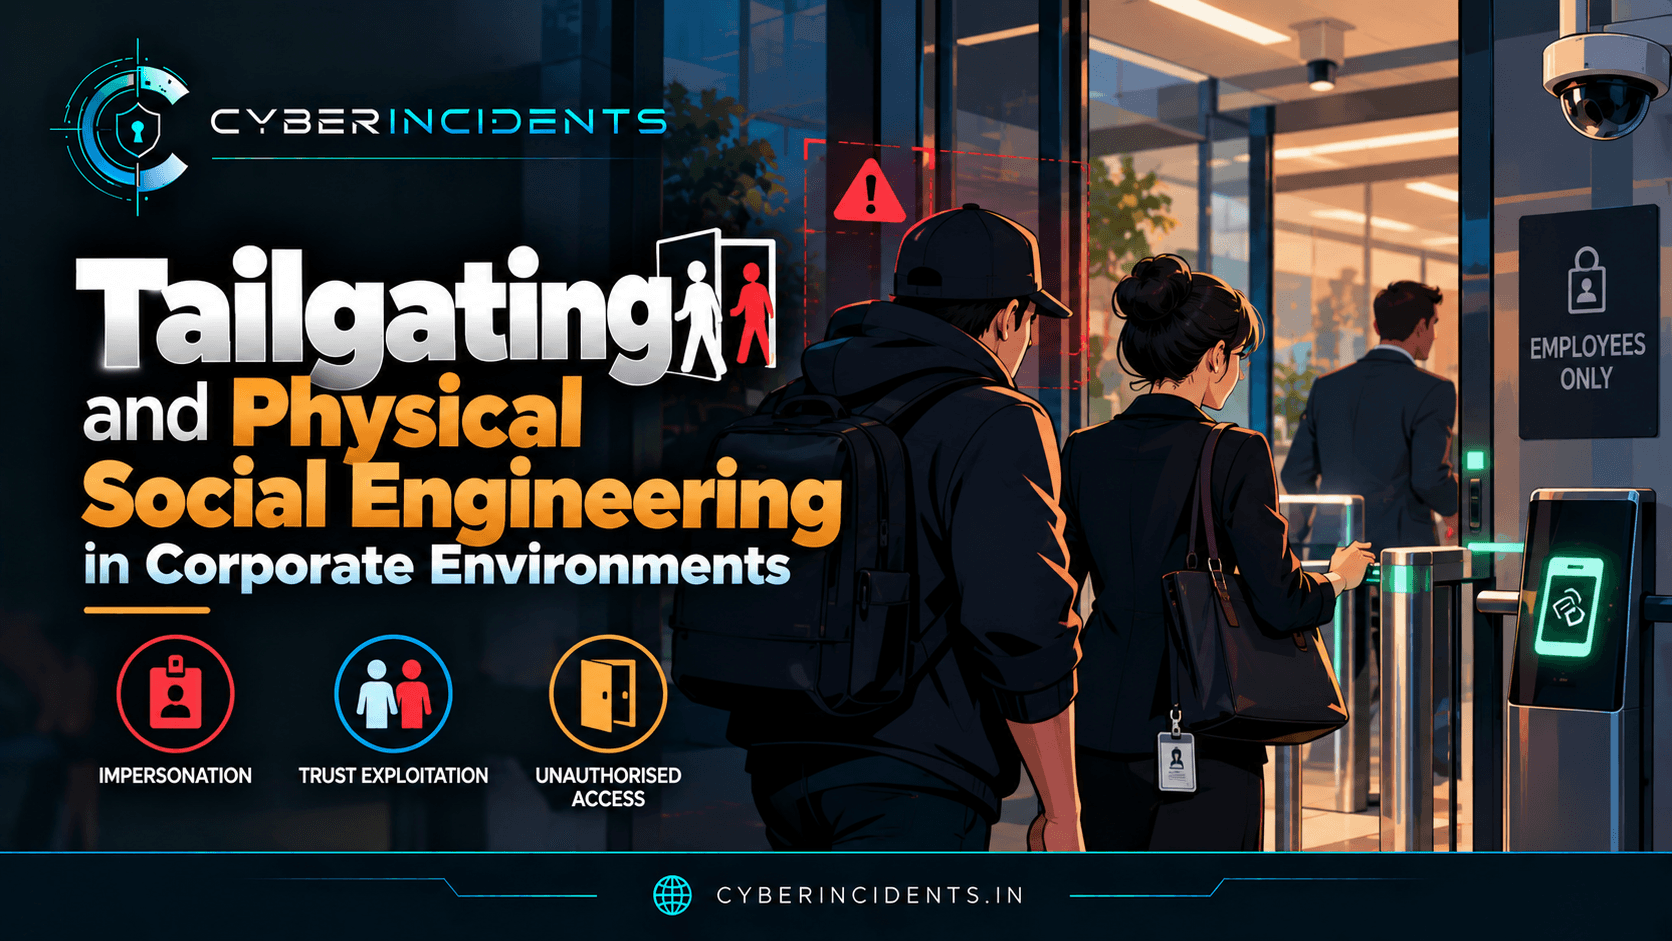
An employee approaches the office entrance, scans their access card, and opens the door. Someone carrying a laptop bag walks closely behind them. The employee assumes the person works in the same building and holds the door open.
Both people enter.
The second person never presented an access card, and nobody verified their identity.
This everyday interaction illustrates tailgating. The unauthorised individual gains access to a controlled area by taking advantage of an authorised person's entry.
The situation may appear harmless. The person could be a new employee, a contractor, or a visitor who forgot their access card. However, without verification, employees cannot reliably distinguish a legitimate colleague from someone deliberately attempting to bypass security.
In a corporate environment, this small lapse can become the first step in a much larger security incident.
2. What Is Tailgating?
Tailgating occurs when an unauthorised individual enters a restricted area by following an authorised person through an access-controlled entrance without independently obtaining permission.
It can happen at office entrances, secure floors, laboratories, data centres, server rooms, and other controlled facilities.
For example, an employee uses an access badge to enter a secure office. An unauthorised person follows through the same door before it closes. The access control system records the employee's valid entry, but the second person may not have been authenticated at all.
Tailgating exploits a gap between technical access controls and human behaviour.
Common contributing factors include:
Employees holding doors open for people they do not recognise.
Busy entrances during shift changes or lunch breaks.
Unverified contractors or visitors entering behind staff.
Employees assuming that someone carrying a laptop or wearing a company badge is authorised.
Weak enforcement of physical access policies.
Tailgating does not necessarily require sophisticated equipment. In many cases, it relies on an ordinary social interaction and the absence of verification.
3. Tailgating vs Piggybacking
The terms tailgating and piggybacking are sometimes used interchangeably, but a useful distinction can help security teams classify incidents.
Tailgating generally describes an unauthorised person entering behind an authorised individual without that person's knowledge or explicit permission.
Piggybacking commonly describes an authorised individual knowingly allowing another person to enter, often out of politeness or a desire to help.
For example, someone may follow an employee through a secured entrance without being noticed. This is typically described as tailgating.
If the employee sees the person and deliberately holds the door open without checking their credentials, the situation is commonly described as piggybacking.
Both behaviours can undermine physical access controls. Organisations should define these terms consistently within their own security policies.
4. How Physical Social Engineering Works
Physical social engineering manipulates human behaviour to gain access to facilities, information, or systems. Rather than exploiting a software vulnerability, the attacker exploits trust, routine, authority, or a person's reluctance to challenge others.
Tailgating is one example, but it can form part of a broader attempt to compromise an organisation.
Scenario 1: The helpful employee
An individual approaches a secured entrance while an employee is entering. The individual asks the employee to hold the door because their hands are full.
The employee wants to be helpful and allows them inside without verifying their identity.
Security weakness: Courtesy overrides the access control procedure.
Scenario 2: The impersonated contractor
Someone claims to be a technician responding to an urgent equipment problem. They present a plausible explanation for needing access to a restricted area.
If employees accept the explanation without checking the work order, identity, and authorisation, the individual may gain access they should not have.
Security weakness: Trust in a claimed role replaces formal verification.
Scenario 3: The unauthorised visitor
A visitor enters the reception area legitimately but moves beyond the authorised visitor zone without an escort.
If employees assume the visitor has already been approved, the individual may reach restricted offices or equipment areas.
Security weakness: Visitor access is not monitored throughout the visit.
Scenario 4: The distracted employee
During a busy period, staff focus on meetings, deliveries, or phone calls. Someone enters a controlled area while attention is elsewhere.
Security weakness: Routine activity and environmental distractions reduce vigilance.
These scenarios demonstrate why physical security needs consistent procedures rather than relying exclusively on employees to make quick judgments.
5. What Happens After Unauthorised Entry?
Tailgating becomes particularly serious when physical access is used to support a wider attack.
Once inside a corporate facility, an unauthorised person may gain opportunities to:
View confidential information left on desks or displayed on screens.
Access unattended laptops or workstations.
Connect an unauthorised device to an available network port, if technical controls permit.
Photograph documents or sensitive equipment.
Enter restricted technical areas.
Search for unsecured storage devices or printed credentials.
Observe employee routines and security procedures.
Physical entry does not automatically provide access to a corporate network or privileged systems. The impact depends on additional safeguards, including locked devices, authentication, endpoint controls, network access restrictions, and the person's actual level of access.
However, physical presence can create opportunities that would otherwise be unavailable to a remote attacker.
6. Investigating a Tailgating Incident
When a suspected tailgating event is reported, physical security personnel and cybersecurity teams may need to work together.
The investigation should establish who entered, where they went, what they accessed, and whether the incident resulted in further security exposure.
Step 1: Establish the initial report
Record when and where the incident occurred, who reported it, and what they observed.
Capture the entrance involved, the approximate number of people, and any available description of the unauthorised individual.
Avoid treating an unverified description as a confirmed identity.
Step 2: Review physical access logs
Examine badge-reader records around the reported time.
Determine which credentials were used, whether access was granted or denied, and whether the number of recorded entries appears inconsistent with the observed movement.
An access log may show an authorised employee entering without recording a second person who followed them.
Important: Badge logs alone may not prove tailgating. Correlate them with CCTV, witness statements, and other available evidence.
Step 3: Examine CCTV footage
Where available and authorised, review footage from relevant entrances, corridors, lifts, and restricted areas.
Establish a timeline of the individual's movements and identify whether they entered areas beyond their authorisation.
Preserve relevant footage according to organisational policy and applicable privacy requirements.
Step 4: Verify visitor and contractor records
Check reception records, visitor badges, appointment schedules, contractor authorisations, and work orders.
Determine whether the individual had a legitimate reason to be present and whether the required checks were completed.
Step 5: Assess possible information or device exposure
Determine whether the individual approached unattended workstations, confidential documents, network ports, server rooms, or other sensitive assets.
If there is evidence of possible device access, involve the SOC or incident response team to review endpoint and authentication telemetry.
Step 6: Correlate physical and cyber evidence
If the event may have resulted in unauthorised system access, examine:
Authentication events around the relevant time.
Unexpected logons or account activity.
Endpoint alerts and suspicious device connections.
Network access control events.
USB device activity, where logged.
Changes to sensitive files or systems.
Correlate timestamps carefully. A physical access incident and a cyber alert occurring at similar times do not automatically establish a causal relationship.
Step 7: Contain and document
Follow organisational procedures to revoke unauthorised access, secure affected areas, protect potentially exposed systems, and escalate confirmed incidents.
Document the timeline, evidence collected, affected assets, containment actions, and recommended improvements.
7. Indicators and Evidence for Security Teams
Unlike malware incidents, tailgating does not produce a universal digital indicator. Investigators must combine physical and technical evidence.
Evidence sourceWhat it may revealBadge-reader logsAccess grants, denials, credential usage, and unusual entry patternsCCTV footageMultiple people entering after one authentication eventVisitor management systemMissing registrations, expired visitor passes, or incomplete check-in recordsSecurity guard reportsUnverified entry attempts and policy violationsEndpoint telemetryPossible workstation access or suspicious device activity following the incidentNetwork access logsUnauthorised or unexpected device connections, where network controls provide visibilityIdentity logsSuspicious account activity that may require correlation with the physical incident
A strong investigation distinguishes confirmed evidence from assumptions. For example, an unregistered person entering a restricted area may establish a physical security breach, but additional evidence is required to conclude that corporate data was accessed or stolen.
8. How Organisations Can Prevent Tailgating
Effective prevention combines employee behaviour, facility design, access management, and technical safeguards.
Enforce individual badge authentication. Every person should use their own authorised credentials. Employees should not assume that someone following them has already been approved.
Train employees to challenge safely. Staff should know how to direct unfamiliar individuals to reception or security without creating unnecessary confrontation.
Use anti-tailgating controls. Where risk justifies the investment, turnstiles, monitored entrances, or mantraps can help ensure that each entry corresponds to an authorised person.
Strengthen visitor management. Register visitors, verify their identities according to policy, issue appropriate visitor badges, and require escorts in restricted areas.
Monitor sensitive zones. Apply stronger access restrictions to server rooms, network equipment areas, laboratories, and locations containing confidential information.
Secure workstations and devices. Use automatic screen locks, strong authentication, device encryption, and appropriate endpoint protections so that physical presence alone does not grant easy access.
Restrict network access. Apply network access control and port security where appropriate. Unknown devices should not automatically receive access to sensitive corporate networks.
Establish a reporting process. Make it easy for employees to report suspicious entry without fear of embarrassment or retaliation for raising a reasonable concern.
Conduct authorised physical security assessments. Use controlled exercises to test whether procedures are followed, document weaknesses, and improve staff awareness. Such assessments should have explicit approval and appropriate safety boundaries.
9. Lessons for Modern Corporate Security
Tailgating illustrates an important principle: cybersecurity and physical security are closely connected.
An organisation may deploy advanced firewalls, endpoint detection and response, multifactor authentication, and centralised monitoring, yet still face risks if unauthorised people can enter restricted areas.
Conversely, strong physical access controls are not sufficient if an unattended workstation remains unlocked or a connected device can access sensitive systems without adequate authentication.
A mature security programme treats physical access, identity management, endpoint protection, and network access as complementary layers.
For SOC teams, physical security reports can provide valuable context when investigating suspicious logons, unexpected device connections, or unexplained activity near sensitive infrastructure.
For security leaders, tailgating is a reminder that procedures must work under everyday conditions, including busy entrances, visitor arrivals, and situations where employees feel social pressure to be helpful.
Conclusion
Tailgating is a simple but potentially serious form of physical social engineering. By exploiting trust and routine, an unauthorised individual may bypass an organisation's entry controls and create opportunities for further security incidents.
Preventing it requires clear access policies, verified visitor management, appropriate physical controls, employee awareness, and strong technical safeguards inside the workplace.
The key lesson: Never confuse physical presence with authorisation. Every person entering a restricted area should have the appropriate permission, and every suspected breach should be investigated using both physical and digital evidence.
Further Reading
NIST — Physical and environmental protection controls within security and privacy control guidance.
CISA — Guidance on physical security and organisational security awareness.
MITRE ATT&CK — Enterprise techniques relevant to physical access, credential access, and subsequent cyber activity.