1. When a QR Code Becomes a Security Threat
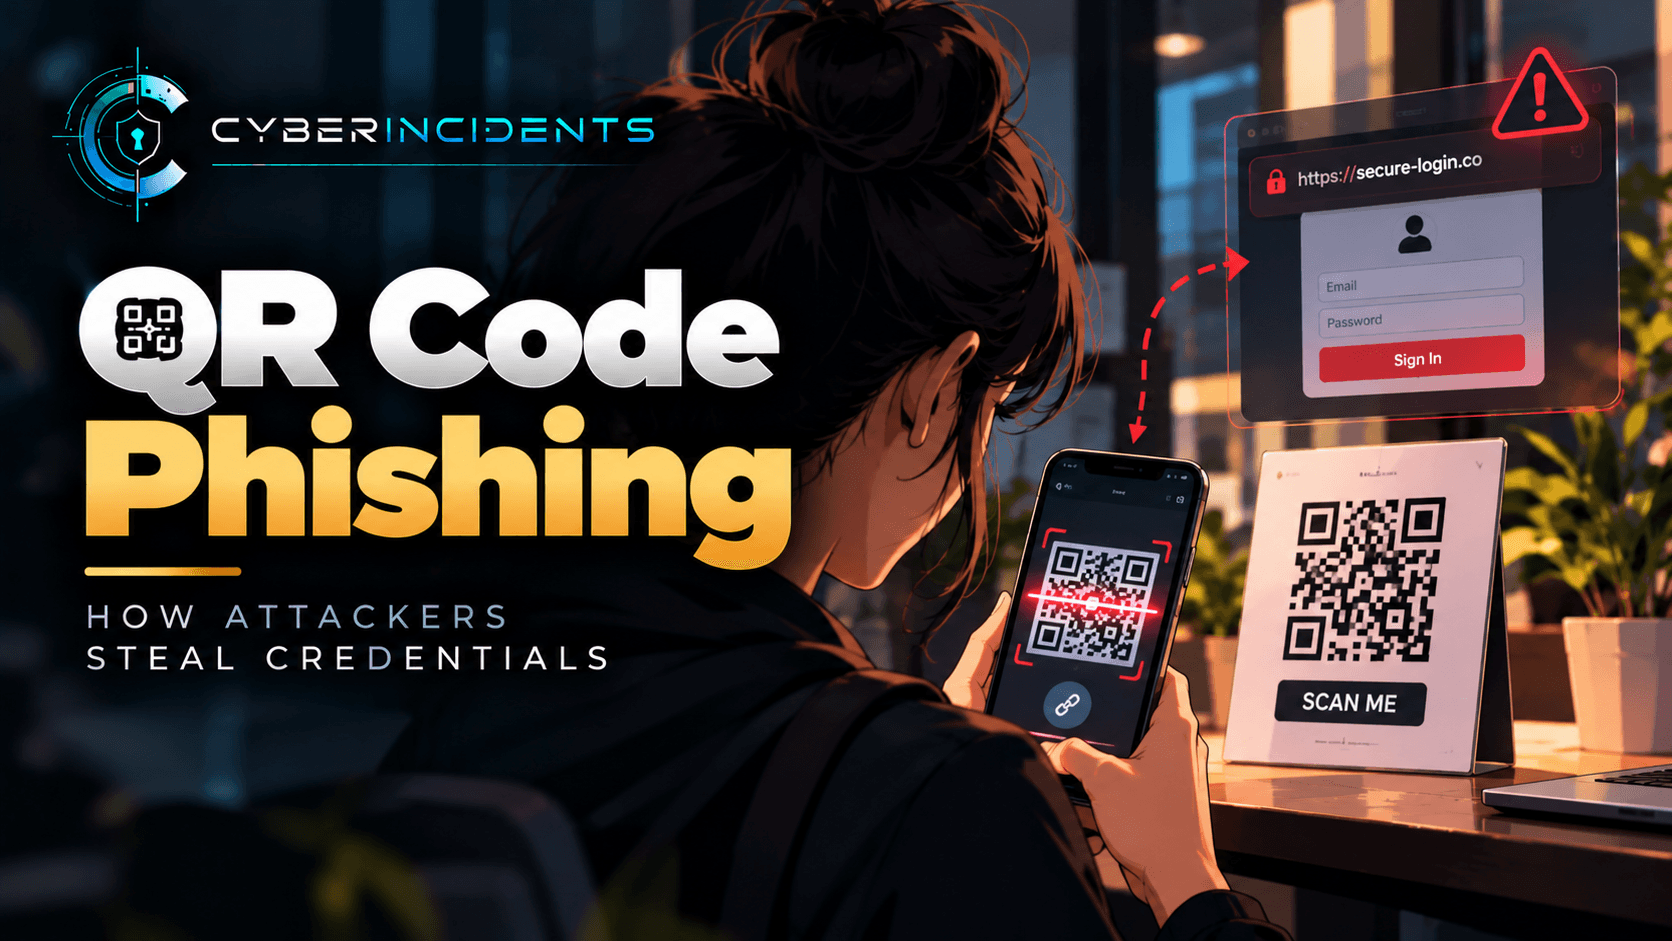
An employee receives an email claiming that their Microsoft 365 account requires verification. The message includes a QR code and instructs the employee to scan it using a mobile phone to prevent account suspension.
The email looks professional. The QR code appears to be a convenient way to access the verification page, so the employee scans it.
The phone opens a website that resembles the company's normal sign-in page. The employee enters their username and password.
The page may display an error or continue to another screen, leaving the employee unaware that their credentials have been exposed.
If the attacker successfully captures and abuses those credentials, they may attempt to access the employee's account and associated corporate resources.
The attack began with a simple image rather than a conventional clickable link.
This is the central risk behind quishing: a QR code can hide a malicious destination behind an action that feels routine and convenient.
2. What Is Quishing?
Quishing is a form of phishing that uses QR codes to direct victims towards malicious or deceptive destinations.
A QR code is a two-dimensional barcode that can encode information such as a website URL, contact details, or other data. Businesses use QR codes legitimately for payments, authentication, menus, document access, and many other purposes.
Attackers exploit this familiarity by placing malicious QR codes in communications that appear trustworthy.
The objective may be to:
Steal corporate usernames and passwords.
Capture authentication information.
Direct users to fraudulent cloud sign-in pages.
Encourage victims to disclose financial information.
Distribute malicious downloads.
Support business email compromise or other account-based attacks.
A QR code is not inherently malicious. The security risk depends on the information it contains, the destination it opens, and what the victim is persuaded to do next.
3. How Does a Quishing Attack Work?
A typical quishing campaign follows several stages, although the exact sequence depends on the attack.
Stage 1: Creating the lure
The attacker prepares a message designed to encourage the victim to scan a QR code.
Common themes include:
Password expiry or account verification.
Multifactor authentication setup.
Shared documents requiring approval.
Invoice or payment confirmation.
Delivery notifications.
Voicemail notifications.
Document-signing requests.
The message often uses urgency or a familiar business process to encourage quick action.
SOC focus: Identify unexpected account-related emails, unusual requests to scan QR codes, and messages that pressure users to act quickly.
Stage 2: Embedding the QR code
The attacker inserts the QR code into an email, image, PDF, document, or printed communication.
Unlike a standard hyperlink, the QR code may not expose its destination in a form that is immediately readable by the recipient.
Some campaigns use QR codes embedded directly in email bodies. Others place them in attachments, making the destination less visible to conventional email-link inspection.
SOC focus: Inspect message bodies and attachments, extract QR codes using approved analysis tools, and decode their embedded destinations in a controlled environment.
Stage 3: Redirecting the victim
When the victim scans the code, their device processes the encoded information. If the code contains a URL, the browser may open the destination.
The destination could be a fraudulent sign-in page, a redirect service, a compromised legitimate website, or another location controlled or abused by the attacker.
A URL may also redirect through multiple destinations before reaching its final page.
SOC focus: Analyse the decoded URL, examine redirect chains safely, and compare the destination with known corporate sign-in domains and trusted threat-intelligence sources.
Stage 4: Stealing credentials
The victim may encounter a fake sign-in page designed to imitate a legitimate cloud service.
If the victim enters credentials, the attacker may collect them. Depending on the attack, the page may also attempt to capture additional authentication information or manipulate the victim into approving an authentication request.
Credential submission does not automatically mean the attacker has successfully accessed the account. Investigators must determine whether the information was used and whether additional protections blocked the attempt.
SOC focus: Correlate the reported scan time with authentication records, suspicious sign-ins, multifactor authentication activity, and account changes.
Stage 5: Attempting account compromise
With captured credentials or other authentication material, the attacker may attempt to access corporate services.
Possible follow-on activity includes accessing email, searching for sensitive documents, creating malicious mailbox rules, or using the compromised account to target additional employees.
These actions are potential consequences, not guaranteed stages of every quishing incident.
SOC focus: Investigate unusual authentication patterns, unexpected mailbox configuration changes, unfamiliar application access, and suspicious activity involving cloud resources.
4. Why Are QR Code Phishing Attacks Effective?
Quishing combines a familiar technology with a deceptive message. Several characteristics can make these campaigns difficult to identify.
The destination is less visible. Recipients may not see the full URL before scanning the code.
Mobile devices are frequently involved. An employee may scan a QR code using a personal phone, while corporate email and identity monitoring operate primarily on managed devices.
Email inspection can be more difficult. A malicious URL embedded in an image may not be as straightforward to inspect as a conventional hyperlink.
The message can look legitimate. Attackers can imitate familiar branding, account notifications, invoices, and document-sharing workflows.
Users may trust the QR code itself. People sometimes assume that a code supplied in a business email has already been checked by the organisation.
The attack can cross device boundaries. The email may arrive on a work computer while the QR code is scanned on a personal mobile device, complicating investigation and visibility.
None of these characteristics makes quishing automatically successful. Email security, URL analysis, identity protection, and user verification can still prevent or limit an attack.
5. Common Types of Quishing Attacks
1. Microsoft 365 and cloud account phishing
An email claims that an employee must verify an account, review a document, or renew access. The QR code opens a counterfeit cloud sign-in page.
The goal is to obtain credentials or other authentication information.
2. Multifactor authentication lures
A message claims that the recipient must scan a QR code to activate or repair multifactor authentication.
The code may lead to a fraudulent setup page or another workflow intended to capture sensitive information.
Employees should use only the organisation's approved authentication setup process.
3. Invoice and payment fraud
A QR code appears on a fraudulent invoice or payment notice and directs the victim to a fake payment portal.
This can overlap with business email compromise when an attacker impersonates a supplier or manipulates payment instructions.
4. Document-sharing scams
A QR code claims to provide access to a shared report, contract, or confidential document.
The victim is directed to a login page that imitates a legitimate cloud service.
5. Physical QR code scams
Attackers may place fraudulent QR code stickers over legitimate codes in public locations or on printed notices.
The replacement code can redirect users to an attacker-controlled destination. The potential consequences depend on the site and what information the victim provides.
6. How SOC Analysts Investigate a Quishing Incident
A successful investigation should establish where the QR code came from, what destination it encoded, whether the user interacted with it, and whether the activity led to account compromise.
Step 1: Collect the original message
Preserve the original email or attachment where possible.
Record the sender, recipient, subject, timestamps, message ID, embedded images, and any associated attachments.
Retaining the original message helps investigators analyse the QR code and correlate the event with email security logs.
Step 2: Extract and decode the QR code
Use an approved QR analysis tool to decode the image and identify its embedded content.
If the code contains a URL, record the full destination and examine any redirects using a controlled analysis environment.
Do not assume that every QR code contains a website. It may encode other types of information.
Step 3: Analyse the destination
Investigate the domain, URL structure, redirect chain, reputation, and relationship to the claimed service.
Look for misspelled domains, unexpected subdomains, suspicious URL shorteners, and destinations unrelated to the stated purpose of the email.
Use approved URL-analysis tools and avoid opening suspicious links directly on a production workstation.
A domain that appears legitimate or has a good reputation is not, by itself, proof that the destination is safe.
Step 4: Determine whether the user scanned the code
Ask the recipient whether they scanned the code, which device they used, what page appeared, and whether they entered information or approved a prompt.
Correlate the reported time with available browser, DNS, secure web gateway, mobile security, and identity logs.
If the code was scanned on an unmanaged personal phone, some technical evidence may be unavailable. Record this limitation rather than assuming that no activity occurred.
Step 5: Investigate possible credential exposure
Review sign-in records for unusual locations, unfamiliar devices, suspicious authentication events, or activity inconsistent with the user's normal behaviour.
In Microsoft Entra ID environments, relevant evidence may be available through sign-in logs, audit logs, and identity-protection alerts, depending on licensing and configuration.
If the victim entered credentials, follow the organisation's compromised-account procedures even if suspicious sign-ins have not yet been detected.
Step 6: Check for post-compromise activity
Examine email and cloud audit logs for suspicious inbox rules, unexpected forwarding, application consent grants, access to sensitive files, or unusual account changes.
Determine whether the compromised account was used to send additional phishing messages.
Step 7: Contain and recover
Depending on the evidence, actions may include removing the malicious email, blocking the confirmed destination, resetting exposed credentials, revoking active sessions, and reviewing multifactor authentication settings.
If a device downloaded or executed malicious content, involve the endpoint response team.
Document the timeline, affected users, evidence, scope, and remediation actions.
7. Indicators and Evidence to Look For
Quishing has no single universal indicator of compromise. Investigators should correlate email, QR code, web, identity, and endpoint evidence.
Evidence sourceWhat to investigateEmail security logsSuspicious messages containing QR codes or image-based luresAttachments and imagesEncoded URLs and unexpected QR codes in documentsURL and DNS logsRequests to suspicious destinations after a reported scanWeb proxy logsRedirect chains and visits to fraudulent sign-in pagesIdentity logsUnusual sign-ins or authentication activity following the scanCloud audit logsUnexpected mailbox changes, application grants, or sensitive resource accessEndpoint telemetrySuspicious downloads or process execution following the incident
A QR code in an email is not automatically malicious. Similarly, visiting a suspicious website does not prove that credentials were entered or stolen. Establish each stage using available evidence.
8. MITRE ATT&CK Mapping
The following techniques may be relevant when supported by evidence. Quishing is a delivery method within the broader phishing landscape, rather than a separate technique that explains every stage of an attack.
TechniqueIDRelevancePhishing: Spearphishing LinkT1566.002A QR code directs a victim to a malicious URLPhishing: Spearphishing AttachmentT1566.001A malicious QR code is delivered inside a deceptive attachmentUser Execution: Malicious LinkT1204.001A victim follows a malicious linkValid AccountsT1078Captured or compromised credentials are used to access servicesEmail Forwarding RuleT1114.003A forwarding rule is abused after mailbox compromise
These mappings depend on the actual behaviour observed. For example, a malicious QR code does not establish that an attacker successfully used valid credentials.
9. How Organisations Can Prevent Quishing
Preventing quishing requires controls that protect users before and after they scan a QR code.
Inspect QR code destinations. Encourage employees to preview the destination before opening it and verify that the domain matches the expected service.
Strengthen email security. Use phishing detection, attachment inspection, URL protection, and image analysis where supported by the security platform.
Protect cloud identities. Enforce multifactor authentication and consider phishing-resistant authentication methods. Monitor unusual sign-ins and account changes.
Secure mobile access. Apply appropriate mobile device management, mobile threat defence, and conditional access policies where feasible.
Train employees. Explain that QR codes can conceal malicious links. Employees should be cautious of unexpected requests to scan codes for account verification, payment, or authentication setup.
Use approved authentication workflows. Employees should initiate account and multifactor authentication setup through official organisational portals rather than following unexpected instructions in an email.
Monitor suspicious activity. Correlate phishing reports, web requests, identity events, and cloud audit activity to identify attacks that progress beyond delivery.
Create a simple reporting process. Make it easy for employees to report suspicious QR codes, even if they have already scanned one.
Prepare an incident response playbook. Define procedures for URL blocking, credential resets, session revocation, affected-account investigation, and evidence preservation.
10. Lessons for Modern SOC Teams
Quishing demonstrates that phishing does not depend on a visible hyperlink or an obvious malicious attachment. A QR code can move the interaction from a monitored corporate computer to a mobile device, creating gaps in security visibility.
For SOC analysts, the investigation must connect the original message with the encoded destination, the user's actions, and any subsequent authentication or cloud activity.
For security engineers, it highlights the value of image-aware email inspection, web filtering, identity monitoring, and mobile security controls.
For employees, the central lesson is that convenience does not establish trust. A QR code should be treated like any other link: its destination and purpose should be verified before sensitive information is provided.
Conclusion
QR code phishing uses a familiar technology to hide deceptive destinations and persuade victims to disclose credentials or perform unsafe actions. By embedding malicious links in emails, attachments, or physical materials, attackers can exploit trust and complicate security monitoring.
Effective defence combines QR code and URL analysis, secure email controls, identity protection, employee awareness, and a well-defined incident response process.
The key lesson: A QR code is simply another way to deliver a link. Verify where it leads before signing in, approving access, or sharing sensitive information.
Further Reading
MITRE ATT&CK — Enterprise techniques for phishing and user execution.
CISA — Guidance on phishing prevention and multifactor authentication.
Microsoft Learn — Microsoft Entra sign-in logs, audit logs, and identity protection.