1. When a Legitimate Permission Request Becomes a Threat
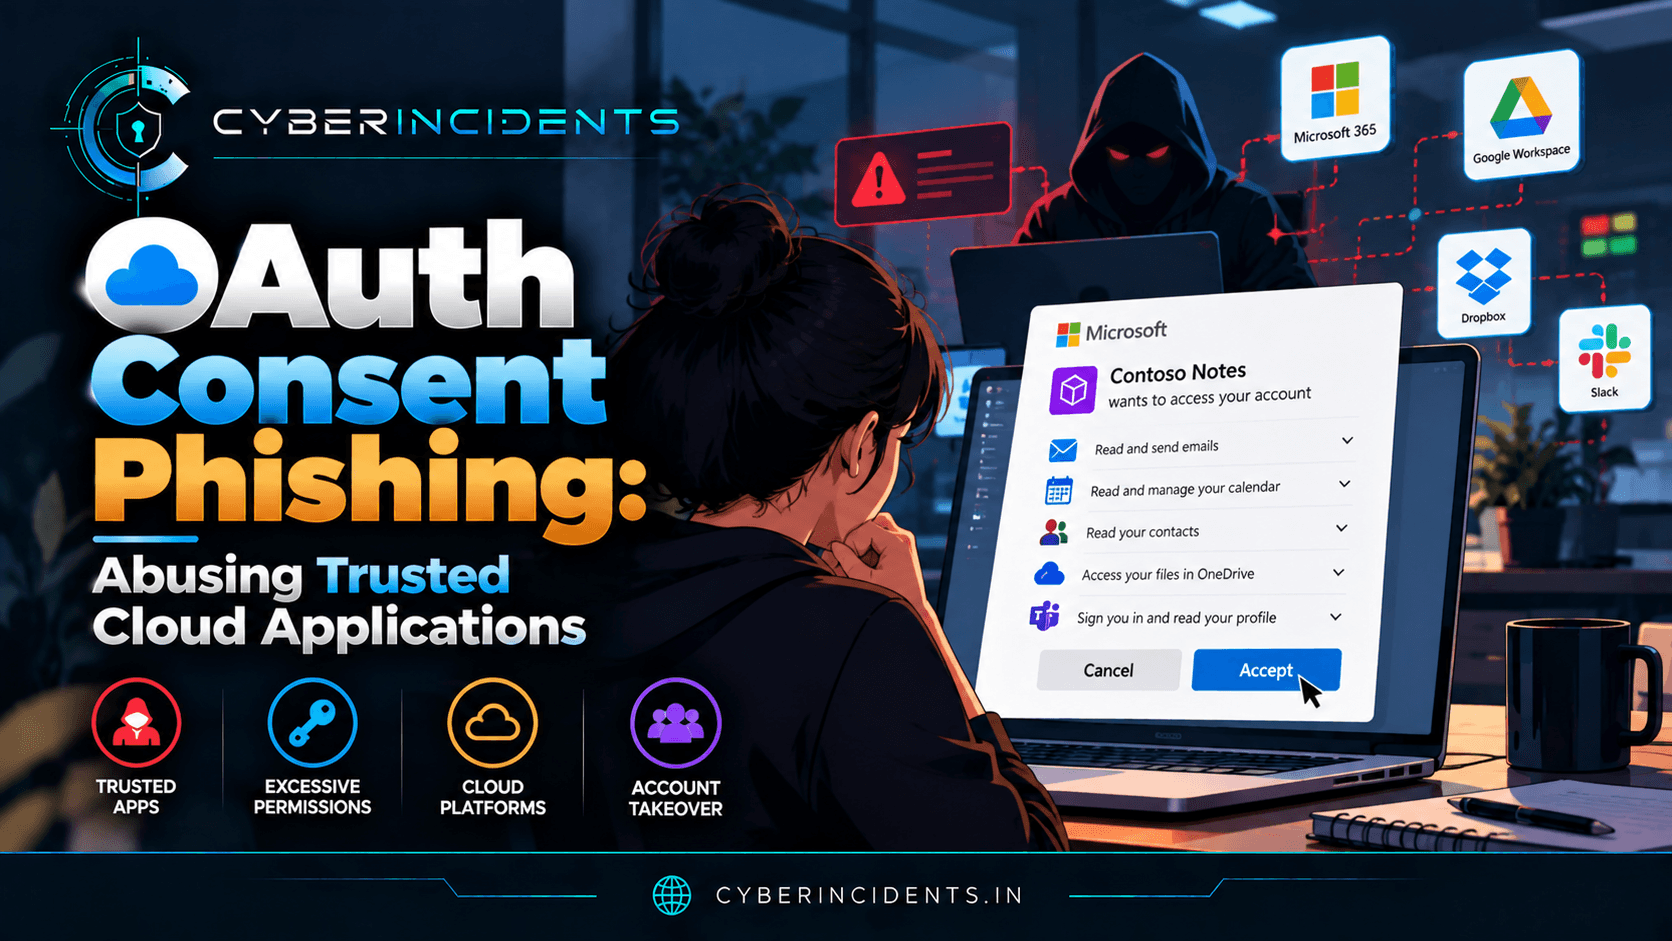
Imagine an employee receives an email inviting them to view an important business document. The link opens a cloud sign-in page, followed by an authorisation screen requesting permission to read their email and access files.
The employee recognises the cloud platform and assumes the request is legitimate. They click Accept.
The sign-in process may appear normal because the authorisation screen belongs to a genuine cloud identity provider. However, the application requesting access is controlled by an attacker.
The attacker may now be able to use the permissions granted to that application to access the victim's resources.
No password necessarily needs to be stolen. The victim has effectively authorised a third-party application to act within the boundaries of the granted permissions.
This is the central risk behind OAuth consent phishing: an attacker abuses legitimate authorisation mechanisms to obtain unauthorised access to cloud resources.
2. What Is OAuth Consent Phishing?
OAuth consent phishing is a social engineering attack that persuades a user to authorise a malicious application to access protected resources.
OAuth 2.0 is an authorisation framework that allows applications to obtain limited access to resources without requiring users to share their passwords directly with those applications.
For example, a legitimate application might request permission to read a user's calendar or access selected files. The identity provider presents the requested permissions, and the user or administrator authorises the application according to the organisation's configuration.
Attackers abuse this workflow by creating or using a malicious application and persuading victims to approve its requested access.
The application may then receive an authorisation grant or token that enables it to request access to permitted resources.
OAuth itself is not the vulnerability. The risk arises when users or administrators grant excessive permissions to an untrusted application, or when an attacker abuses an existing application or consent configuration.
3. How Does an OAuth Consent Phishing Attack Work?
An attack can involve several stages, from application preparation to accessing cloud data.
Stage 1: Preparing a malicious application
The attacker creates or controls an application that requests access to cloud resources.
The application may use a name, description, or branding designed to appear trustworthy. It might resemble a document viewer, productivity tool, meeting application, or business integration.
A convincing display name does not establish that the application is legitimate.
SOC focus: Examine the application's publisher information, application ID, creation details where available, requested permissions, and organisational approval status.
Stage 2: Delivering the lure
The attacker sends a message inviting the victim to review a document, access a shared file, or use a business application.
The link directs the user into an authorisation workflow. Unlike a traditional fake login page, the consent screen may be hosted by the real cloud provider.
SOC focus: Investigate the original message, URL, sender, and destination application. Correlate email delivery with subsequent identity events.
Stage 3: Requesting permissions
The application asks for permissions, often expressed as scopes or API access rights.
Depending on the platform and the permissions requested, these may include access to profile information, email, files, calendars, or other resources.
The permissions displayed to the user can be difficult to evaluate, particularly when the request appears to be associated with a familiar business task.
SOC focus: Determine exactly which permissions were requested and which were granted. Do not treat every OAuth consent event as malicious.
Stage 4: The victim grants consent
The user approves the request, or an administrator grants permissions where administrative consent is required.
The identity platform records the relevant authorisation activity. The application may then be able to obtain tokens or use an existing authorisation grant to access permitted resources.
The exact flow depends on the identity provider, application type, consent configuration, and permissions involved.
SOC focus: Identify the consenting user or administrator, the application involved, the requested permissions, and the time of the consent event.
Stage 5: Accessing cloud resources
If the authorisation is successful, the application may use its granted access to interact with cloud APIs.
Depending on the permissions, the attacker may attempt to read emails, access files, inspect calendars, or collect other information available through the authorised application.
OAuth consent does not automatically grant unrestricted access to an entire tenant. The application's effective access depends on its permissions, the identity and resources involved, and the platform's authorisation controls.
SOC focus: Review subsequent API activity and determine which resources were accessed. Look for unusual access patterns and activity inconsistent with the application's intended purpose.
Stage 6: Maintaining or expanding access
An attacker may attempt to continue using the authorised application or combine the access with other compromised identities and resources.
The persistence mechanism depends on the application's grants and the cloud platform. Revoking a password alone may not remove every application authorisation or active token.
SOC focus: Review application permissions, service principals, refresh-token or session behaviour where available, and any additional account or application changes.
4. Why Is OAuth Consent Phishing Difficult to Detect?
Traditional phishing investigations often focus on stolen credentials, suspicious sign-ins, or malware execution.
OAuth consent phishing can follow a different path. A user may authenticate successfully and approve an application through a legitimate identity-provider workflow.
This creates several investigative challenges.
Legitimate infrastructure: The authorisation page may belong to a genuine cloud provider, so its domain alone may not indicate malicious activity.
No obvious password theft: The attacker may obtain application access without learning the user's password.
Valid tokens: Requests made using valid authorisation tokens may resemble legitimate application activity.
Permission complexity: Employees may not understand the implications of granting access to email, files, or other resources.
Multiple audit sources: Investigators may need to correlate email security, identity-provider, application audit, and API activity to reconstruct the incident.
The important distinction is that successful authentication does not necessarily mean that every application involved in the session is trustworthy.
5. OAuth Consent Phishing vs Traditional Credential Phishing
Although both attacks can begin with a deceptive message, they exploit different aspects of cloud identity.
FeatureTraditional credential phishingOAuth consent phishingPrimary objectiveObtain passwords or other authentication secretsObtain application authorisation or permissionsTypical user actionEnter credentials into a deceptive pageApprove an application permission requestPossible attacker accessUse stolen credentials to attempt sign-inUse granted application access within its effective permissionsCommon investigation focusAuthentication failures, suspicious sign-ins, and credential useConsent events, application permissions, token activity, and API accessPotential remediationReset compromised credentials and revoke sessions as appropriateRevoke malicious grants, disable or remove the application where appropriate, and investigate affected identities and resources
The two techniques can also occur together. A phishing campaign may steal credentials and later persuade the victim to approve a malicious application.
6. How SOC Analysts Investigate OAuth Consent Phishing
A structured investigation should establish whether the application is malicious, identify the permissions granted, determine what resources were accessed, and remove unauthorised access.
Step 1: Validate the alert
Review the alert from the identity platform, cloud security service, SIEM, or application monitoring system.
Collect the available details, including:
Application name and application ID.
User or administrator who granted consent.
Consent timestamp.
Requested and granted permissions.
Publisher and verification information.
Associated sign-in and audit events.
A newly authorised application may be legitimate. Validate the event against the application's business purpose and approval records.
Step 2: Inspect the application and permissions
Review the application's configuration and determine whether its permissions are appropriate for its stated function.
Investigate unexpected requests for email access, file access, directory information, or other sensitive resources.
Distinguish delegated permissions, which generally operate in the context of a user, from application permissions, which can permit an application to act independently of a signed-in user and may require administrative consent.
The effective risk depends on the platform and the specific permissions granted.
Step 3: Review identity-provider audit logs
Examine the consent event and surrounding identity activity.
In Microsoft Entra ID environments, relevant evidence may be available through audit logs, sign-in logs, and enterprise application records.
Determine whether the consent followed a suspicious email, an unusual sign-in, or other activity associated with the suspected attack.
Step 4: Investigate application activity
Review available application and cloud audit records for unusual access after consent was granted.
Depending on the platform and permissions, examine:
Unexpected email or file access.
API requests inconsistent with the application's purpose.
Access to resources outside the user's normal activity.
Unusual activity involving multiple users.
Repeated access continuing after the original consent event.
The absence of a suspicious interactive sign-in does not rule out application-based access.
Step 5: Determine the scope
Identify every affected user, application, service principal, permission grant, and potentially accessed resource.
Establish whether the incident involved one user's delegated access or broader application permissions affecting multiple resources.
Check whether sensitive information may have been accessed or exported. Do not claim data exfiltration without supporting evidence.
Step 6: Contain the threat
Where the application is confirmed malicious or unauthorised, follow the organisation's response procedures to revoke its permissions or grants, disable the application, and block further access where appropriate.
Consider revoking affected user sessions or tokens when necessary. Coordinate with cloud administrators because application changes can affect legitimate business services.
Step 7: Recover and strengthen controls
Review the initial delivery method, user interaction, and permission settings that enabled the incident.
Remove unnecessary application access, verify the status of affected accounts, improve consent restrictions, and monitor for renewed activity.
Document the timeline, evidence, scope, containment actions, and lessons learned.
7. Indicators and Evidence to Look For
OAuth consent phishing does not have a universal indicator of compromise. Investigators should correlate application, identity, and resource-access evidence.
Evidence sourceWhat to investigateIdentity audit logsUnexpected consent grants and application permission changesEnterprise application recordsUnknown applications, unfamiliar publishers, and suspicious service principalsSign-in logsUnusual authentication activity preceding or following consentCloud audit logsUnexpected access to email, files, directories, or other resourcesEmail security logsMessages and links associated with the authorisation requestApplication permissionsExcessive or unexplained access relative to the application's purposeToken and session recordsUnusual application access and continued activity after the suspected compromise
An unfamiliar application name or a large number of permissions is not sufficient by itself to prove malicious activity. Investigators must validate the application's ownership, purpose, approval status, and actual use.
8. MITRE ATT&CK Mapping
The following techniques may be relevant when supported by incident evidence. The exact mapping depends on how the attacker obtained and used application access.
TechniqueIDRelevancePhishing: Spearphishing LinkT1566.002A deceptive link directs a victim to a malicious authorisation workflowAdditional Cloud CredentialsT1098.001Relevant when an attacker adds or abuses cloud credentials as part of persistenceSteal Application Access TokenT1528Relevant when application access tokens are stolenCloud AccountsT1078.004Relevant when compromised cloud accounts are usedCloud Service DashboardT1538Relevant when attackers use cloud service interfaces during an intrusion
These techniques should not be assigned automatically to every OAuth consent incident. A malicious consent grant does not necessarily mean that credentials or tokens were stolen.
9. How Organisations Can Prevent OAuth Consent Phishing
Effective prevention focuses on limiting which applications can receive access and making suspicious authorisation activity visible.
Restrict user consent. Configure identity platforms so that users can authorise only appropriate applications under clearly defined conditions. Require administrator approval for sensitive or unverified applications where appropriate.
Review application permissions. Regularly audit enterprise applications, service principals, consent grants, and unused integrations.
Assess publishers and applications. Validate the application's publisher, ownership, purpose, and requested permissions before approval.
Apply least privilege. Grant only the minimum permissions needed for an application to perform its intended function.
Monitor consent activity. Alert on unexpected application registrations, unusual permission grants, suspicious consent events, and changes to sensitive application configurations.
Protect identities. Use strong authentication, monitor risky sign-ins, and investigate suspicious activity around the time of a consent grant.
Educate employees. Explain that a legitimate cloud authorisation screen does not guarantee that the application requesting access is trustworthy.
Review existing grants. Remove unnecessary permissions and investigate applications that have no clear business owner or purpose.
Prepare an incident response process. Establish how to revoke application access, review affected resources, preserve audit evidence, and coordinate cloud recovery.
10. Lessons for Modern Cloud Security
OAuth consent phishing demonstrates that cloud security is not limited to protecting usernames and passwords.
Applications can become trusted pathways to sensitive resources. If an application receives excessive permissions or is approved without proper review, an attacker may exploit that trust to access information through legitimate cloud mechanisms.
For SOC teams, this means monitoring not only user authentication but also the applications users authorise, the permissions those applications receive, and the resources they access afterward.
For cloud administrators, the priority is to maintain visibility into application identities and ensure that permissions remain aligned with business requirements.
For employees, the lesson is straightforward: before approving an application, verify who provides it, why it needs access, and whether the requested permissions make sense.
Conclusion
OAuth consent phishing abuses a legitimate cloud authorisation process to obtain access through malicious or untrusted applications. Because the user may successfully authenticate and the authorisation page may be genuine, the incident can be difficult to distinguish from normal cloud activity without examining application permissions and subsequent resource access.
Defending against this threat requires restricted consent policies, least-privilege permissions, application governance, audit-log monitoring, and a clear process for revoking malicious access.
The key lesson: Trust in the cloud platform does not automatically make every application trustworthy. Investigate the application, verify its permissions, and monitor what it accesses after authorisation.
Further Reading
Microsoft Learn — Microsoft Entra application consent and permissions.
MITRE ATT&CK — cloud account and application-access techniques.
CISA — cloud identity security and phishing mitigation guidance.