Cyber News
TeamViewer Vulnerability Allows Remote Hosts to Crash or Execute Code on Connected Computers
Vulnerability / Endpoint Security
7 min read
Cyber Espionage / Artificial Intelligence
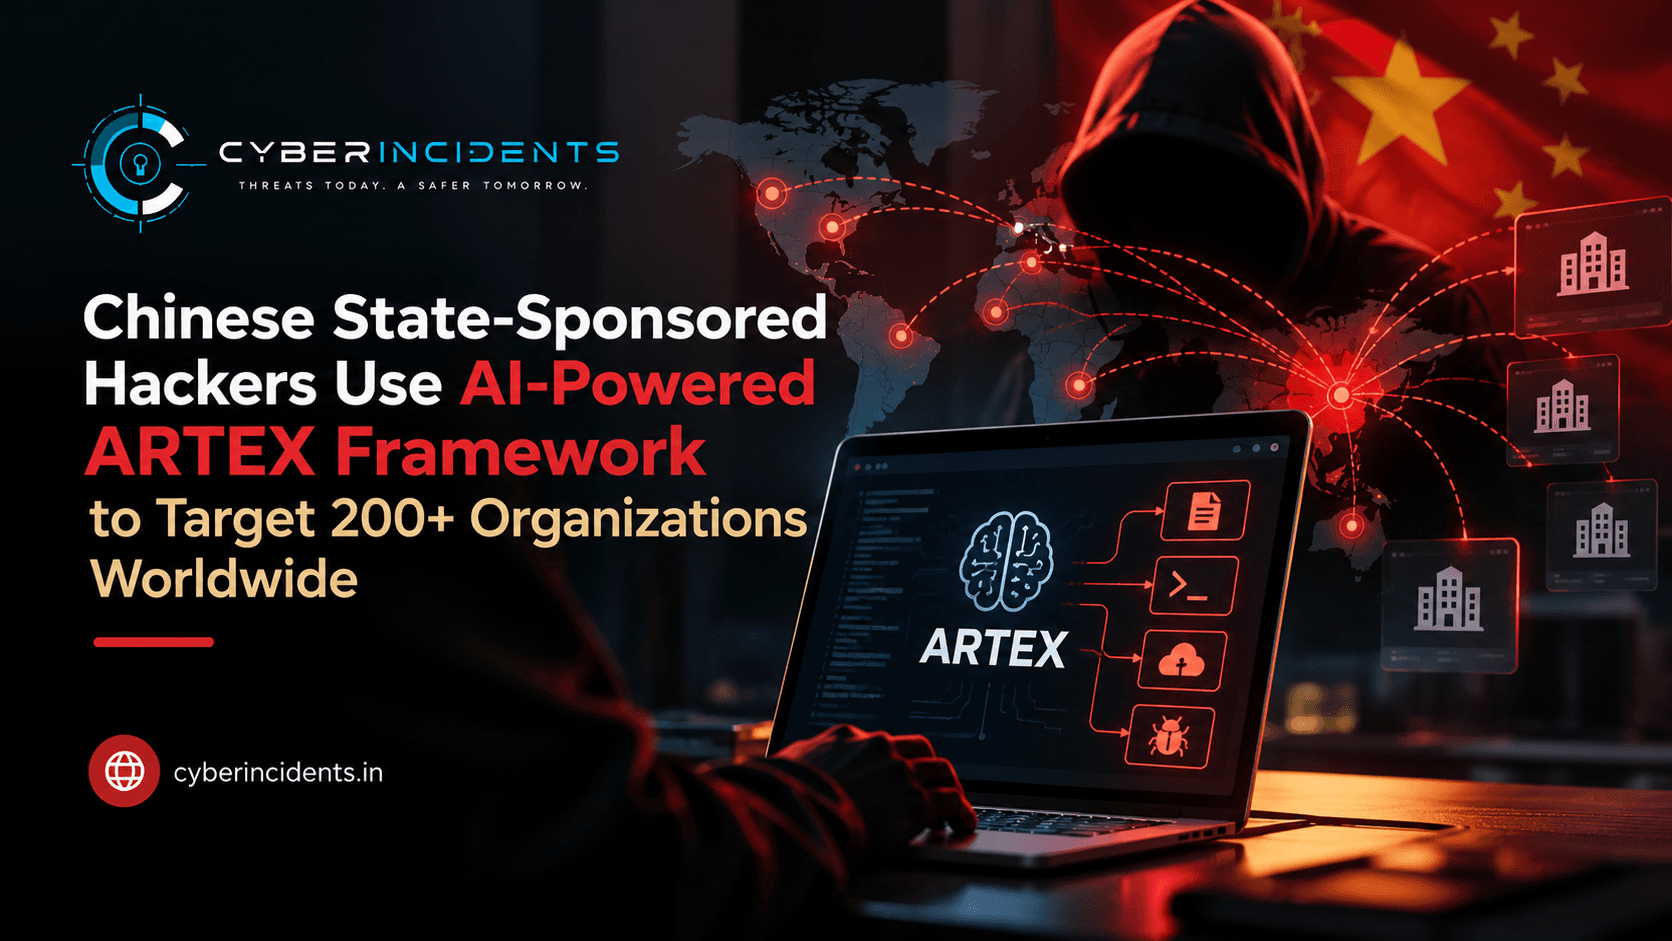
A China-linked threat actor tracked by CrowdStrike as Vapor Panda (formerly VexatiousTemper) has been observed using an AI-powered penetration-testing framework called ARTEX to conduct coordinated cyber-espionage operations against more than 200 organizations worldwide.
The campaign, observed from October 17, 2026, demonstrates how agentic AI can automate reconnaissance, vulnerability identification, exploitation, credential theft, and lateral movement across multiple environments.
The attackers combined ARTEX with DeepSeek and an unidentified subscription-based commercial large language model (LLM). Multiple AI agents worked together under human supervision to pursue different attack paths simultaneously.
Threat actor: Vapor Panda (China-linked, state-sponsored).
Primary tool: ARTEX (Go-based AI-powered penetration-testing framework).
Campaign start: October 17, 2026.
Organizations targeted: More than 200 worldwide.
Confirmed post-exploitation activity: Nine organizations.
Malware deployed: BLOODALCHEMY, described as a derivative of ShadowPad.
Primary objectives: Cyber espionage, credential theft, reconnaissance, privilege escalation, and lateral movement.
Key concern: AI-assisted automation allows a relatively small operator team to conduct multiple complex intrusions simultaneously.
CrowdStrike has attributed a large-scale cyber-espionage campaign to Vapor Panda, a China-based targeted intrusion adversary previously tracked as VexatiousTemper.
The group, first identified in February 2021, has overlaps with the threat cluster known as Earth Estries, documented by Trend Micro.
Beginning October 17, 2026, Vapor Panda reportedly used ARTEX to target more than 200 distinct organizations across several countries and industries.
The targeted organizations included:
Government: Foreign ministries, interior ministries, presidential offices, prime minister's offices, defense, justice, finance, and intelligence entities.
United States: 19 organizations across pharmaceutical, semiconductor, defense, nuclear, and financial sectors.
Telecommunications: Providers in the United States, Belgium, and the Philippines.
Research and policy: Think tanks and other organizations of strategic interest.
The campaign demonstrates a shift toward using agentic AI to coordinate established intrusion techniques across a significantly wider target base.
ARTEX is a Go-based AI-powered penetration-testing framework designed to coordinate multiple AI agents to perform reconnaissance, vulnerability identification, exploitation, and other intrusion activities.
In this campaign, the attackers reportedly combined ARTEX with DeepSeek and an unidentified commercial LLM.
The framework used two primary types of agents:
Planner agents: Coordinate the overall operation, determine objectives, and assign tasks.
Worker agents: Execute individual tasks such as reconnaissance, vulnerability identification, exploitation, and lateral movement.
A human operator remained involved throughout the operation, directing agents toward specific objectives and reviewing or steering their actions.
According to CrowdStrike, the agents were instructed to perform activities including:
Writing web shells.
Extracting domain administrator passwords.
Enumerating endpoint security sensor coverage.
Identifying vulnerable systems and services.
Exploring alternative attack paths.
Conducting internal reconnaissance and lateral movement.
CrowdStrike reported that planning agents consumed approximately 1.4 billion input tokens during a single intrusion, illustrating the scale of automated activity.
The significance is not simply that attackers are using AI to write malicious code. ARTEX enables multiple attack paths to be investigated and pursued concurrently, reducing the amount of manual effort required to manage complex intrusion operations.
CrowdStrike confirmed post-exploitation activity at nine organizations.
During these intrusions, Vapor Panda deployed BLOODALCHEMY, a malware family described as a derivative of ShadowPad.
Following deployment, attackers conducted activities including:
Credential spraying.
Network scanning.
Internal reconnaissance.
Further discovery of systems and access opportunities.
The campaign also involved credential-scanning and password-spraying activity against at least 12 additional organizations, including U.S.-based think tanks and European government entities.
CrowdStrike's analysis of recovered ARTEX transcripts revealed several attack paths spanning cloud environments, web applications, containers, Active Directory, email, and VPN infrastructure.
1. Cloud Metadata Access and Privilege Escalation
One observed attack chain involved combining an unsigned Security Assertion Markup Language (SAML) assertion with an XML External Entity (XXE) vulnerability.
The attackers used this combination to query the cloud Instance Metadata Service (IMDS).
The reported sequence involved:
Exploiting the authentication and application vulnerabilities.
Accessing cloud instance metadata.
Obtaining a role capable of issuing administrative commands to thousands of instances.
Escalating access to recover an enterprise administrator account.
This demonstrates the potential impact of weaknesses in application authentication, XML processing, and cloud identity permissions when exploited together.
2. Web Shell Deployment and Active Directory Abuse
Another attack path involved multiple techniques across application infrastructure and enterprise identity systems.
The observed activities included:
Deploying web shells.
Abusing an unauthenticated orchestration service to obtain root access in a production container environment.
Reading Local Administrator Password Solution (LAPS) passwords.
Abusing resource-based constrained delegation (RBCD) to impersonate a privileged account.
These activities could provide attackers with deeper access to internal infrastructure and privileged identities.
3. Abuse of Long-Lived Authentication Keys
CrowdStrike also identified an engagement where the attackers supplied ARTEX agents with authentication keys that had reportedly not been rotated since 2022.
The agents used these keys to forge an administrator token and access mailboxes.
The operation subsequently expanded into VPN infrastructure:
VPN configurations were recovered from a user's sent email.
A VPN client key associated with a purported May 2024 email leak was identified.
The recovered configuration and key were used to reach the internal network.
This highlights the risk of long-lived credentials, insufficient key rotation, and sensitive authentication material being retained in email communications.
One of the most significant findings is how ARTEX coordinates different attack paths simultaneously.
Rather than following a single linear exploitation sequence, agents can investigate web applications, cloud services, container environments, Active Directory, email systems, and VPN infrastructure in parallel.
When an approach fails, the agents can explore alternative methods.
The human operator remains responsible for directing the operation and instructing the agents to pursue particular objectives.
This combination of autonomous execution and human supervision can increase the operational scale of an intrusion campaign without requiring a proportionate increase in human operators.
The report also discusses several other China-linked threat clusters identified by CrowdStrike.
Overcast Panda
Overcast Panda has been associated with close-access intrusions targeting individuals travelling to China. The group reportedly deployed its proprietary FlowCloud backdoor through direct physical access to victims' devices.
FlowCloud uses DLL sideloading and legitimate cloud infrastructure for command-and-control communications.
Its reported capabilities include:
Keylogging.
Screen capture.
File collection.
Credential harvesting.
Persistent remote access.
Titan Panda
Titan Panda has been observed targeting legal organizations through vulnerabilities involving hard-coded IIS machine keys in Intapp Time Server.
The activity, first detected in April 2026, reportedly enabled remote code execution against affected organizations.
Following exploitation, attackers deployed an in-memory framework called IceGiant for reconnaissance, persistence, lateral movement, and data exfiltration.
The report states that the activity affected several North American legal organizations and that the threat actor has been operational since at least 2021.
These activities illustrate the broader range of techniques associated with China-linked espionage operations, although they should not be treated as part of the same ARTEX campaign without supporting evidence.
The supplied reporting does not provide confirmed IP addresses, domains, file hashes, or specific command-and-control indicators for the ARTEX campaign.
The following malware and framework names are useful investigation pivots:
| Name | Description |
|---|---|
ARTEX | Go-based AI-powered penetration-testing and intrusion framework |
BLOODALCHEMY | Malware deployed during confirmed Vapor Panda post-exploitation activity; described as a ShadowPad derivative |
ShadowPad | Malware family referenced in the BLOODALCHEMY relationship |
FlowCloud | Overcast Panda backdoor associated with a separate China-linked campaign |
IceGiant | In-memory framework associated with Titan Panda activity |
These names are threat-intelligence pivots, not standalone indicators of compromise. The presence of a penetration-testing framework or a related tool name does not independently establish malicious activity.
Investigate authentication telemetry across Active Directory, Microsoft Entra ID, VPN infrastructure, and other identity providers.
Look for:
Repeated authentication failures across multiple accounts.
Authentication attempts originating from the same source against numerous users.
Successful logins following repeated failures.
Password-spraying patterns targeting privileged accounts.
Unusual authentication activity involving service accounts or administrative identities.
Correlate authentication events with endpoint and network telemetry to identify potential compromised accounts.
Review web server logs, endpoint telemetry, and application security events for suspicious file creation and execution.
Prioritize:
Unexpected executable files in web-accessible directories.
Unusual child processes spawned by web server processes.
Web server processes launching shells or scripting engines.
Unexpected outbound connections from application servers.
Unusual access to internal services following web application exploitation.
Correlate these events with application vulnerabilities and authentication activity.
Investigate unexpected access to cloud Instance Metadata Services from application workloads and containers.
Look for:
Unusual metadata-service requests.
Unexpected retrieval or use of temporary cloud credentials.
Suspicious role assumption activity.
Privileged API operations following metadata access.
Unexpected administrative actions across multiple cloud instances.
Correlate metadata access with cloud audit logs, workload identity activity, and changes to cloud permissions.
Review Active Directory telemetry for suspicious delegation changes and privileged account activity.
Investigate:
Unexpected resource-based constrained delegation configurations.
Unusual service-account behaviour.
Unexpected access to LAPS-managed credentials.
Suspicious privileged account impersonation.
Unusual authentication patterns involving domain administrators.
Correlate these findings with endpoint process execution and directory-service changes.
Review Kubernetes audit logs, container runtime telemetry, and orchestration service activity.
Prioritize:
Unauthenticated requests to orchestration APIs.
Unexpected container creation or modification.
Containers obtaining root privileges unexpectedly.
Suspicious access to Kubernetes service accounts and secrets.
Unusual communication between workloads and internal services.
Monitor endpoints and servers for suspicious deployment or execution of known malware families, including BLOODALCHEMY.
Investigate unusual file creation, DLL loading, persistence mechanisms, and outbound network connections.
Use threat-intelligence enrichment and endpoint telemetry to validate findings rather than relying exclusively on malware names.
Investigate suspicious access to mailboxes and the presence of sensitive authentication material in email communications.
Look for:
Unusual mailbox access and message searches.
Access to old emails containing VPN configurations or authentication keys.
Unexpected VPN authentication using previously inactive credentials.
Unusual access following the use of long-lived authentication keys.
Prioritize the rotation of exposed keys and investigate related identity activity.
Traditional detection approaches may focus on individual tools or commands. However, agentic frameworks can coordinate legitimate administrative utilities and multiple attack techniques.
Security teams should therefore correlate behaviours across several stages:
External reconnaissance and vulnerability discovery.
Initial access through web or cloud weaknesses.
Credential and secret discovery.
Privilege escalation.
Internal network and service enumeration.
Lateral movement and persistence.
Data access and potential exfiltration.
The combination of these activities can be more meaningful than identifying a single AI framework or executable.
Strengthen cloud identity security: Apply least-privilege permissions to cloud roles and regularly review role assignments.
Secure Instance Metadata Services: Restrict unnecessary metadata access and enforce appropriate workload identity protections.
Protect Active Directory: Monitor delegation configurations, privileged accounts, and LAPS access.
Rotate long-lived credentials: Establish regular rotation policies for authentication keys, VPN credentials, and other sensitive secrets.
Secure application infrastructure: Patch exposed web applications and validate authentication and XML-processing controls.
Harden container environments: Require authentication for orchestration services and restrict container privileges.
Improve credential-spraying detection: Monitor authentication failures across multiple accounts and correlate them with successful sign-ins.
Protect email and VPN infrastructure: Monitor sensitive mailbox access and investigate unexpected VPN authentication.
Strengthen endpoint visibility: Monitor web shells, suspicious process execution, DLL sideloading, and unexpected administrative activity.
Adopt behaviour-based detection: Correlate activity across identity, endpoint, cloud, network, and application telemetry instead of depending solely on static indicators.
Prepare for AI-assisted attacks: Evaluate whether SOC workflows can detect multiple parallel attack paths and rapidly changing attacker techniques.
Continue reading
Cyber News
Vulnerability / Endpoint Security
Cyber News
Vulnerability / Network Security
Cyber News
Identity Security / Artificial Intelligence
3 entries, most recent posts.
Vulnerability / Endpoint Security
Vulnerability / Network Security
Homograph attacks