When Android Malware Starts Thinking Like a Criminal
Imagine a banking trojan that does more than steal credentials. It collects messages from infected phones, captures information entered into fake banking screens, and helps criminals decide which victims are worth pursuing first.
That is the concerning development described in Cleafy's investigation of RatHat, an Android banking trojan whose operators manage infections through a web-based control console.
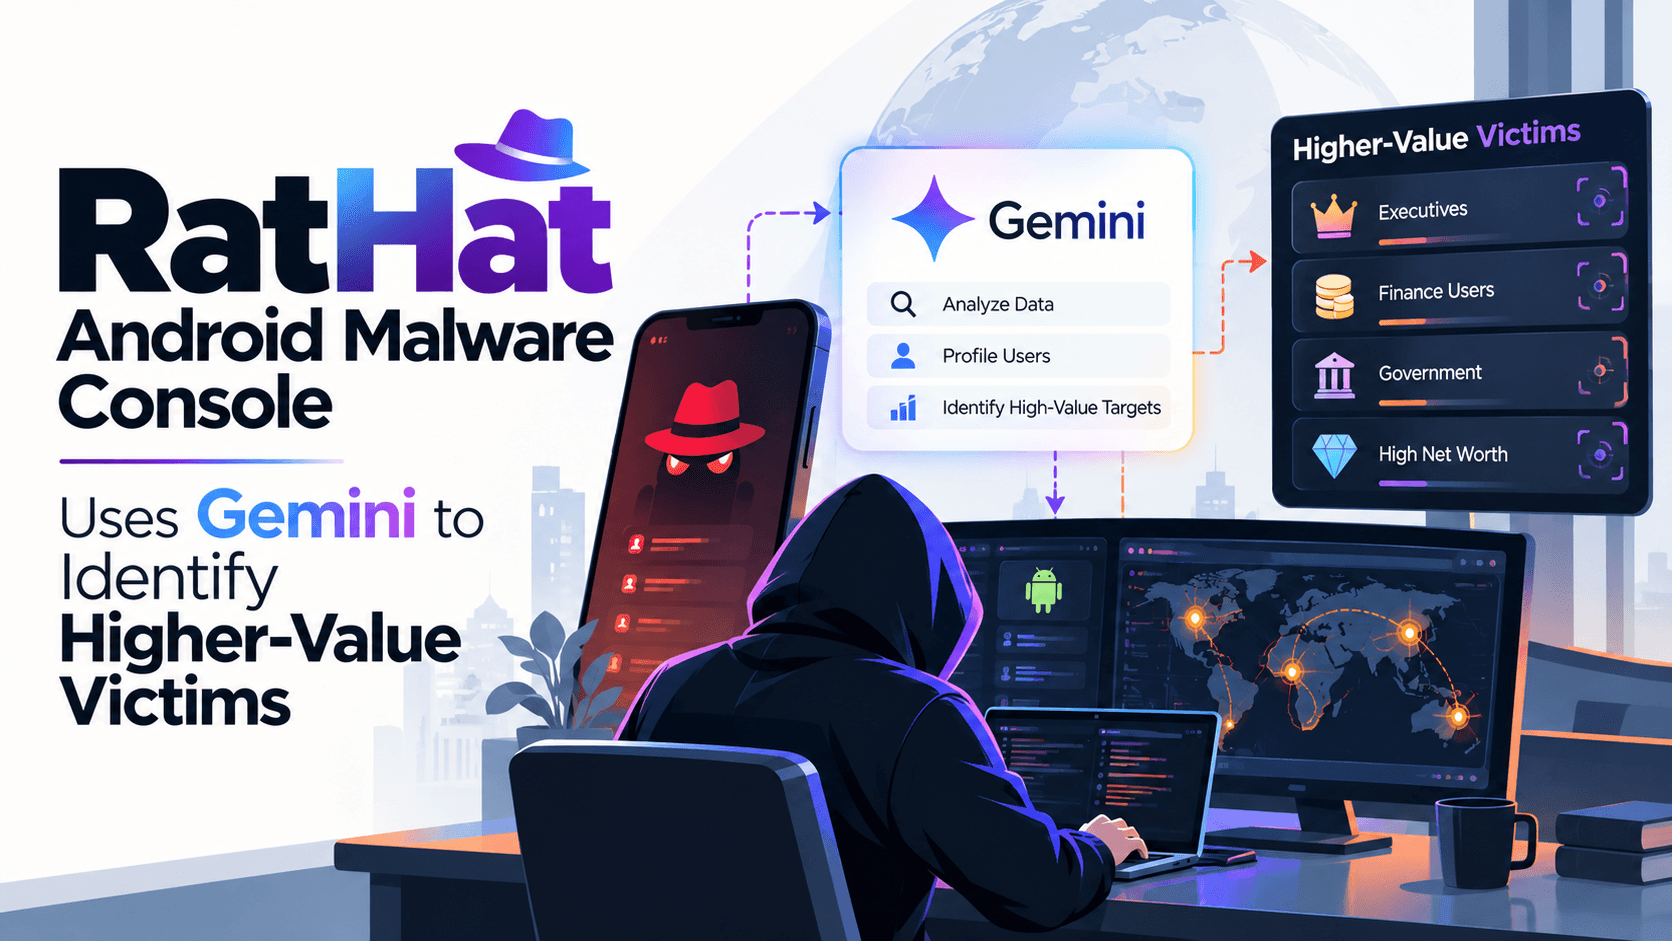
The console does not simply provide access to compromised devices. Its newer versions incorporate Google's Gemini AI model to estimate victims' financial value based on information collected from their messages. The console then groups victims into high-value and mid-value categories.
According to Cleafy, the AI is being used to help operators prioritize victims—not to execute financial transfers itself.
This distinction matters. Artificial intelligence is not necessarily replacing the malware's underlying functionality. Instead, it is helping criminals make decisions using data that the malware has already collected.
What Is RatHat?
RatHat is an Android remote-access and banking malware platform associated with a malware-as-a-service (MaaS) model.
In this model, developers maintain the malware and its control infrastructure, while different operators can use their own deployments to target victims. Cleafy reported tracing nearly 100 RatHat console deployments since April 2026.
The platform combines several capabilities:
Malware building: Operators can generate Android applications containing the malicious payload.
Application disguise: The malware can be packaged inside applications designed to appear harmless.
Command and control: Operators can manage infected devices through a web interface.
Credential collection: The malware can capture information entered into fake login screens and collect messages.
Remote interaction: Operators can monitor device screens and, under certain conditions, interact with them remotely.
AI-assisted prioritization: The console uses Gemini to estimate which victims may have greater financial value.
This combination turns the platform into more than a simple credential stealer. It provides operators with a workflow for building, distributing, managing, and exploiting infected devices.
Three Console Versions, One Evolving Operation
Cleafy's investigation identified changes in the infrastructure used to control RatHat.
Earlier samples from late 2025 and February 2026 connected to a console called Fisher. Between April and September 2026, researchers identified three newer versions.
Console versionReported periodBlackCat Remote Control ManagementApril 2026Panda Workshop V5August 2026Panda Workshop V6September 2026
Despite their different names, the three newer consoles reportedly share the same underlying codebase.
The console also acts as a malware-building environment. Operators can generate a malicious application, sign it, and publish it to Amazon S3 or a web server without manually managing the hosting process.
Another feature allows applications to be rebuilt on a schedule, potentially as frequently as once an hour. Each rebuild creates a different file from the same malware, making it harder for security tools that rely primarily on known file hashes to recognize every version.
The console also introduced templates for fake download pages, including one called Google Store.
These capabilities illustrate how a malware platform can automate multiple stages of an operation rather than requiring an operator to manage each step manually.
How RatHat Reaches Victims
According to the supplied report, RatHat is distributed through text messages and online advertisements that redirect users to third-party download sites.
The victim is encouraged to install an application that appears legitimate. Once installed, the malicious application requests Accessibility access.
Android Accessibility services are designed to help users interact with their devices. Depending on the granted capabilities, they can allow an application to read information displayed on the screen or perform actions on the user's behalf.
When abused by malware, these capabilities can support credential theft and unauthorized interaction with banking applications.
RatHat uses Accessibility access to help enable wireless debugging, read the pairing code displayed on the device, and connect to Android Debug Bridge (ADB).
ADB is a legitimate Android debugging interface. In this case, the malware abuses it to establish a shell running as Android's shell user, identified by UID 2000.
That shell provides capabilities beyond those normally associated with the application's own permissions.
The important security lesson is that a legitimate operating-system feature can become part of a malicious attack chain when an application tricks a user into granting access and then abuses the resulting capabilities.
Remote Control Without the Usual Recording Indicator
RatHat's remote-control functionality is one of the more technically significant elements of the report.
Cleafy found that operators can deploy a separate program written in Go through the console. The program remains reachable through a reverse tunnel initiated by the infected phone, allowing an operator to connect through the established communication channel.
The deployment is not entirely automatic: although ADB pairing occurs automatically, the Go program runs only after the operator clicks the deploy button.
Once deployed, the program changes how the attacker can observe and interact with the device.
The normal screen-capture route
Screen capture through the malicious application uses an Android feature that requests permission from the victim and displays a recording indicator while capture is active.
This creates a visible sign that screen recording is taking place.
The alternative remote-control route
The separate Go program uses tools named minicap and minitouch to stream screen content and simulate touch interactions. According to Cleafy, this method can operate without the same permission prompt and recording indicator.
However, the report identifies an important limitation: minicap and minitouch do not work on Android 14 and later. On those devices, the malware falls back to its own screen-capture mechanism, which displays the relevant permission prompt.
Cleafy also described a backup approach using screencap at approximately five frames per second, although the report did not specify which Android versions support that fallback.
Another concern is persistence. The Go program reportedly continues running after the victim removes the original application, until the device restarts. Zimperium also found that the program can reinstall the application and re-enable its Accessibility access.
The supplied reports do not provide a confirmed, complete removal procedure. Consequently, removing the visible application alone should not automatically be considered proof that a device is clean.
How Gemini AI Helps Identify Valuable Victims
The most notable feature in the newer console is its use of Gemini AI to evaluate victims.
RatHat collects information from infected devices, including text messages and credentials entered into fake login screens displayed over banking applications. The console can then use the collected messages to estimate the victim's bank balance.
Based on this estimate, victims are categorized into high-value and mid-value groups.
For the operator, this changes the economics of a malware campaign. Instead of reviewing every infected device with equal attention, the attacker can prioritize devices that appear more financially attractive.
The AI therefore acts as a decision-support component within the criminal operation.
Gemini also runs on the infected phone
The console's AI integration serves a second purpose.
RatHat contains predefined instructions for interacting with specific device manufacturers' interfaces, Android versions, and languages. These instructions can fail when the infected phone behaves differently from what the malware authors anticipated.
When that happens, the malware can send the screen layout to Gemini and ask where it should tap next. It calls Gemini directly from the phone using an API key stored in its settings.
Cleafy said this functionality is used to help maintain the wireless-debugging setup.
The report also notes that the console's AI integration changed over time. The earliest version supported multiple AI providers and could send Telegram alerts when a victim's AI score crossed a configured threshold. The latest version reportedly uses Gemini exclusively and directs operators to Google AI Studio to obtain an API key.
These are two distinct uses of AI:
Neither capability means the AI independently controls the entire attack. Both operate within a larger system built and configured by the malware's developers.
What This Means for Android Security
RatHat highlights several risks that defenders and users should understand.
First, Accessibility access deserves careful scrutiny. The feature is legitimate and important for many users, but granting it to an untrusted application can expose powerful interaction capabilities.
Second, wireless debugging can become an attack path. Users and security teams should investigate unexpected debugging activity, particularly when it follows the installation of an unfamiliar application or suspicious Accessibility requests.
Third, file-based detection alone may be insufficient. Scheduled rebuilds can produce different hashes while preserving the same underlying malicious functionality. Behavioural detection and infrastructure correlation can help identify related samples.
Fourth, AI can make stolen data more actionable. The addition of victim scoring demonstrates how criminals can use AI to prioritize information already obtained through conventional malware techniques.
Finally, removing an application may not resolve every component of an infection. In this case, the separate Go program reportedly persists until a device restart and may reinstall the malicious application. Incident responders should validate device state and investigate persistence rather than relying exclusively on the visible app list.
SOC Investigation: What Should Analysts Look For?
The following checks are defensive recommendations based on the capabilities described by Cleafy and Zimperium. They are not claims that every RatHat infection will generate every indicator.
1. Investigate suspicious application installations
Review Android telemetry, mobile threat-defense alerts, and available installation records for applications installed through unfamiliar websites, text-message links, or suspicious advertisements.
Correlate installation events with the timing of Accessibility permission grants and other unexpected device changes.
2. Review Accessibility and debugging activity
Look for unusual applications receiving Accessibility access and investigate unexpected activation of wireless debugging or ADB pairing.
Where telemetry permits, correlate these events with device-management records, application identities, and network activity.
3. Monitor suspicious process and file activity
Cleafy specifically identified minicap and minitouch under /data/local/tmp after deployment of the remote-control component.
Investigate these files in context, particularly if they appear alongside unexplained shell activity associated with UID 2000 or unexpected remote-control connections. These filenames alone are not proof of malware because legitimate development and testing environments may use the same tools.
4. Correlate command-and-control indicators
Search network, DNS, proxy, and mobile threat-defense telemetry for the domains and IP address listed in the indicators section below.
Check the timing of connections against application installation, ADB activity, and suspicious screen-interaction behaviour. Use the historical version and date associated with each indicator to avoid overlooking infrastructure changes.
5. Assess potential credential and financial exposure
If RatHat is suspected or confirmed, determine whether the user accessed banking applications or entered credentials while the device was compromised.
Follow the organization's incident-response process to assess possible exposure of banking credentials, one-time passwords, messages, and other sensitive information. Coordinate with the affected user and financial institution where appropriate.
6. Validate containment and recovery
Preserve relevant evidence before making changes where feasible. Isolate the device according to incident-response procedures, revoke or reset potentially exposed credentials, and verify whether the remote-control component or other persistence mechanisms remain.
Because the supplied research does not provide a complete removal procedure, use a trusted mobile incident-response process to determine whether the device can be reliably cleaned or needs a more comprehensive recovery.
Indicators of Compromise (IOCs)
The following indicators were listed by Cleafy in the supplied report. Defenders should preserve the reported version and date context when using them in threat-intelligence platforms or detection rules.
Command-and-Control Infrastructure
IndicatorReported associationadmin.chunhuating[.]bestPanda Workshop V6 — September 2026admin.xiongmaocs[.]picsPanda Workshop V5 — August 20268.231.120[.]246BlackCat — April 2026admin.rathat[.]liveFisher — December 2025 and February 2026
Distribution URLs
URLReported contexthxxps://dramaspoolcoa[.]com/en.htmlDownload link — September 2026hxxps://rathat[.]me/app-release-rat-hat-live.apkDownload link — December 2025 and February 2026
File Hashes
MD5Reported sample date116346cace7f00ba557034b534d40791September 20268fdc21e25097a46528211274e54330e1February 2026f83357b2d47c7d38ee53943373961211December 2025
Host and Behavioural Indicators
Files named minicap and minitouch located under /data/local/tmp following deployment of the reported remote-control component.
Unexpected shell activity associated with Android UID 2000.
Unusual wireless debugging and ADB pairing activity following suspicious application installation.
Unexpected Accessibility permission grants to unfamiliar applications.
Suspicious application rebuilds, remote-control connections, or communication with the listed infrastructure.
Cleafy also observed console domains beginning with admin. and, for the latest version, an adminapi. backend pattern. The report describes use of inexpensive top-level domains, including .best, .beer, and .top.
These patterns are useful for investigation but should not be treated as universal RatHat indicators. Domain patterns and tools can also appear in legitimate environments.
Conclusion
RatHat demonstrates how Android malware is evolving beyond credential collection and remote access. Its operators combine application-building automation, abuse of Android debugging features, persistent remote-control capabilities, and AI-assisted victim prioritization within a single platform.
Gemini does not need to execute a bank transfer to increase the effectiveness of an attack. By helping operators identify potentially more valuable victims and navigate unfamiliar device interfaces, AI can improve the efficiency of an operation that still relies on traditional malware capabilities.
For defenders, the priority is to connect the evidence: suspicious app installation, Accessibility abuse, wireless debugging, shell activity, remote-control tools, and communication with known infrastructure. Detecting one component is useful, but understanding the complete attack chain is what enables effective containment and recovery.