1. Introduction: What Happens When an Attack Reaches an Endpoint?
An employee receives an email containing what appears to be a legitimate business document. After opening it, an unexpected script executes, launches a command-line utility, and attempts to contact an unfamiliar external server.
The attack may not immediately produce a recognisable malware file. It may instead rely on legitimate operating-system tools, suspicious process relationships, or activity that appears harmless when examined individually.
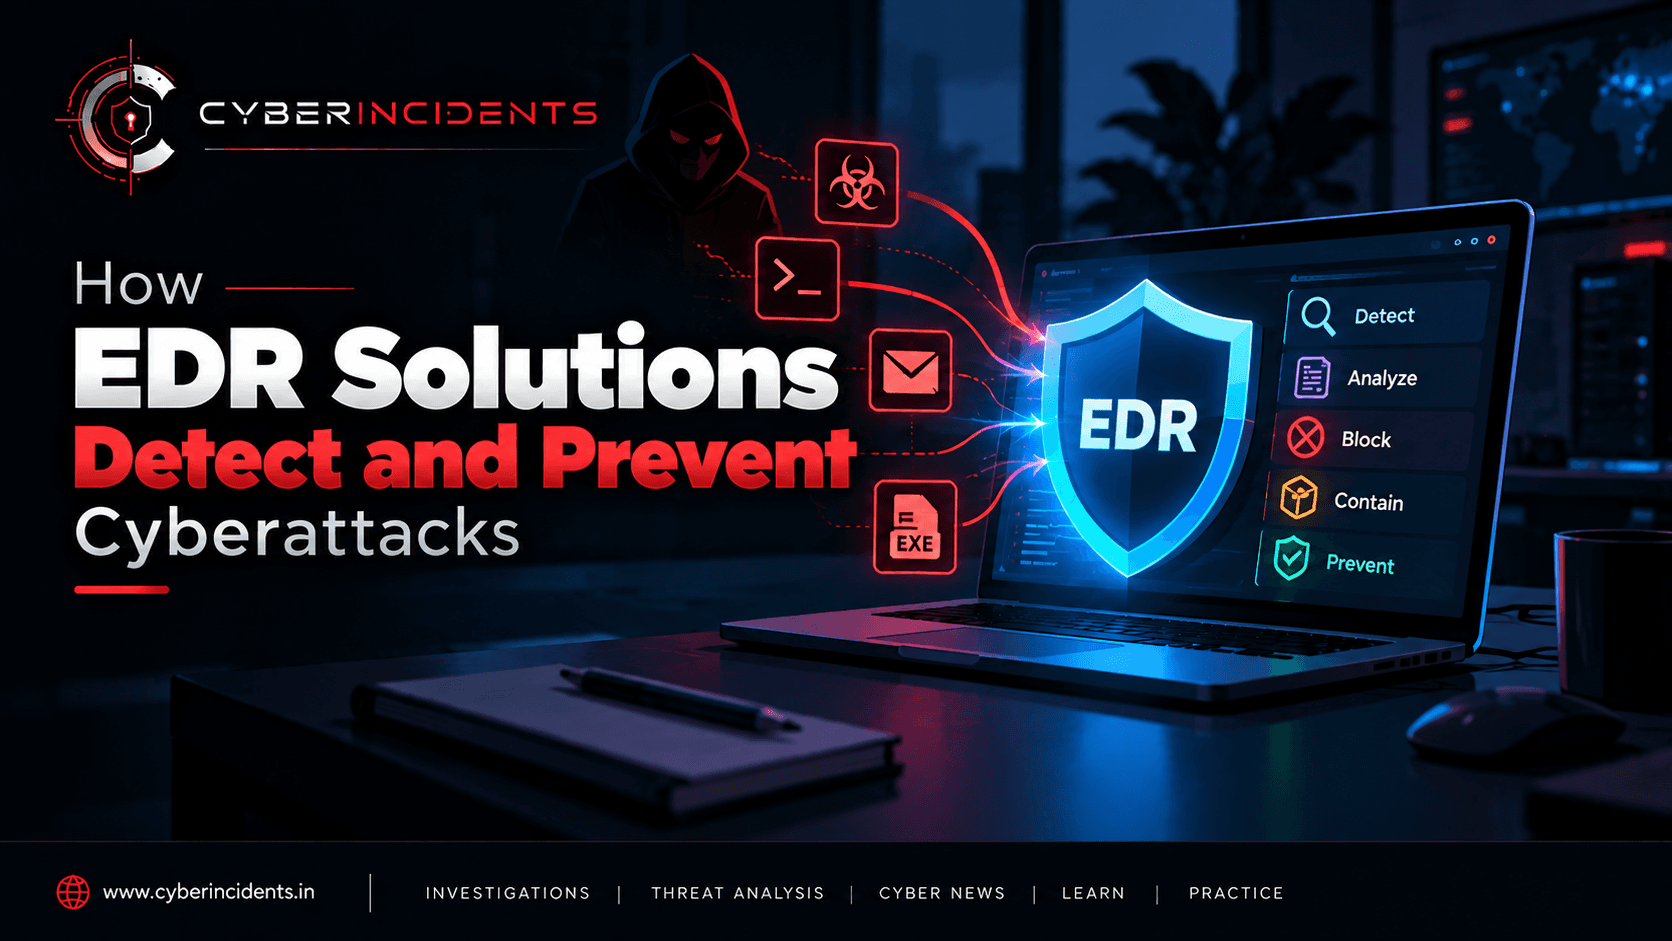
This is where Endpoint Detection and Response becomes valuable.
An EDR solution collects endpoint telemetry, evaluates activity against detection logic, and helps security teams identify suspicious sequences of events. Rather than focusing exclusively on whether a file matches a known malware signature, it can examine how processes behave, what they modify, and how they communicate.
For a Security Operations Centre (SOC), EDR provides visibility into what happened on an endpoint and, when supported by the product, capabilities to contain the threat before it spreads.
2. What Is EDR?
Endpoint Detection and Response is a security technology designed to detect, investigate, and respond to suspicious activity on devices such as laptops, desktops, and servers.
EDR typically uses an endpoint agent or sensor to collect security-relevant telemetry and send it to a management platform for analysis. The platform may apply behavioural analytics, detection rules, threat intelligence, and automated response policies.
Core capabilities commonly include:
Endpoint monitoring: Collecting information about processes, files, user activity, and network connections.
Threat detection: Identifying suspicious patterns using signatures, rules, behavioural analytics, or machine-learning models.
Investigation: Reconstructing process trees and timelines to understand the scope of an incident.
Threat hunting: Searching endpoint telemetry for indicators or behaviours that may not have generated an alert.
Response and containment: Supporting actions such as process termination, file quarantine, and endpoint isolation, depending on product capabilities and permissions.
EDR is different from traditional antivirus, although the capabilities can overlap. Antivirus often focuses on preventing or detecting known malicious files and other threats. EDR adds deeper behavioural visibility, investigation workflows, and response capabilities.
EDR is also distinct from Extended Detection and Response (XDR), which typically correlates signals across multiple security domains, such as endpoints, identity, email, and network infrastructure.
3. How EDR Works: From Telemetry to Response
<AsyncImage query="professional cybersecurity endpoint detection response architecture diagram endpoint agent telemetry analytics security operations center response" aspectRatio="16:9" width="100%" />
A typical EDR workflow follows several stages.
Stage 1: Endpoint telemetry collection
The EDR sensor collects information about security-relevant activity on the device. Depending on the operating system and product, this may include:
Process creation and command-line arguments.
Parent-child process relationships.
File creation, modification, and deletion.
Registry modifications on Windows.
Network connections and DNS-related activity.
Security alerts and suspicious behaviour.
Selected authentication or system events.
For example, an EDR platform may record that Microsoft Word launched PowerShell, which then created a file and initiated an outbound network connection.
That sequence provides more investigative context than a single alert stating that PowerShell ran.
Stage 2: Detection and analysis
The platform analyses collected telemetry using one or more detection methods.
Signature-based detection: Compares files or other artefacts against known malicious patterns.
Behavioural detection: Identifies activity that resembles suspicious or malicious behaviour, such as an unexpected process attempting to modify security settings.
Rule-based detection: Applies explicit conditions or correlations to events, such as a suspicious process launching a script interpreter followed by an unusual network connection.
Machine-learning-assisted analysis: Uses statistical or learned patterns to identify potentially malicious activity. Its effectiveness depends on the model, available telemetry, and the environment.
Some EDR platforms also incorporate threat intelligence to enrich detections with information about known malicious files, domains, or infrastructure.
No single detection method is sufficient for every attack. Combining multiple methods helps cover both known threats and previously unseen behaviours.
Stage 3: Alert generation
When activity meets a detection condition, the platform may generate an alert.
An alert can contain the affected endpoint, user, process, file path, command line, timestamp, detection rationale, and related events.
Some platforms group related alerts into a single incident. This can help analysts distinguish an attack sequence from unrelated events occurring on the same device.
The presence of an alert does not automatically confirm a successful compromise. Analysts must validate the evidence, determine the likely cause, and assess the impact.
Stage 4: Investigation and correlation
EDR tools commonly provide process trees, event timelines, file details, and related telemetry to help investigators reconstruct what occurred.
An analyst might discover the following sequence:
An unexpected document process launches PowerShell.
PowerShell creates a suspicious script or executable.
The new process attempts an outbound connection.
A registry autorun entry is modified.
The EDR platform detects suspicious behaviour.
Correlating these events helps the analyst determine whether they are related and whether the activity indicates execution, persistence, command-and-control communication, or another attack stage.
Stage 5: Containment and remediation
Depending on the product, licensing, configuration, and analyst permissions, EDR may support actions such as:
Isolating an endpoint from the network while retaining a management connection.
Terminating a malicious process.
Quarantining or removing a malicious file.
Blocking identified indicators.
Collecting additional forensic evidence.
Initiating a guided remediation workflow.
Automated actions can reduce response time, but high-impact containment decisions should follow the organisation's incident-response policies.
4. Behavioural Detection: Identifying Attacks Without Relying Only on Malware Signatures
Modern attacks may use modified malware, scripts, legitimate administration tools, or techniques that do not produce a conventional malicious file.
EDR can help identify such activity by analysing behaviour and context.
Example: Suspicious PowerShell execution
A user opens a document, which launches PowerShell with unusual command-line arguments. The process subsequently creates a file in a temporary directory and contacts an unfamiliar domain.
An EDR investigation may correlate:
The document application's process.
PowerShell execution details.
The file creation event.
The associated network connection.
Any follow-on process activity.
Each event has legitimate uses in isolation. The combined sequence, however, may warrant investigation.
Example: Credential-access behaviour
A process attempts to access a sensitive process or perform activity associated with credential theft. Depending on sensor visibility and detection logic, EDR may identify the suspicious behaviour and associate it with the initiating process.
The analyst should review process access telemetry, privilege context, related alerts, and subsequent account activity before concluding that credentials were successfully accessed or stolen.
Key principle: Behavioural detection focuses on what a program does, not only what the program is called or whether its file hash is already known.
5. Detecting Common Attack Techniques
EDR platforms can help detect activity associated with multiple stages of an attack. Actual coverage varies by product, operating system, configuration, and available telemetry.
Attack behaviourWhat EDR may observeInvestigation focusMalicious executionSuspicious process creation or file executionOrigin, parent process, command lineScript abuseUnexpected PowerShell or script-interpreter activityScript content, user context, follow-on actionsPersistenceRegistry, service, or scheduled-task changesWhether the change is authorised and what it launchesProcess injectionSuspicious memory access or execution patternsSource process, target process, related behaviourCredential accessBehaviour associated with accessing sensitive processes or credential storesProcess identity, privilege context, corroborating eventsRansomware activityRapid file modifications, suspicious encryption-like behaviour, or related detectionsScope, affected files, process attributionCommand-and-controlSuspicious process-linked outbound connectionsDestination, timing, DNS activity, process behaviourDefence evasionAttempts to interfere with security controls or monitoringWhether the attempt succeeded and what visibility was lostLateral movementSuspicious remote execution or related endpoint activitySource and destination systems, identity events
These are investigation opportunities, not guarantees that every EDR product will detect every technique.
6. How EDR Helps Detect Ransomware
Ransomware is a clear example of how endpoint behavioural detection can support early intervention.
Depending on the ransomware family and the product's detection capabilities, suspicious indicators may include:
Rapid modification or renaming of many files.
Unusual access to large numbers of documents.
Creation of ransom notes.
Attempts to interfere with backups or security controls.
Suspicious process chains preceding widespread file changes.
An EDR solution may detect this behaviour and block a process or isolate an endpoint before the attack affects additional systems.
However, detection and prevention are not guaranteed. Some ransomware can encrypt files before an alert is generated, and legitimate applications may also modify large numbers of files.
A sound investigation should determine which process performed the changes, how many files were affected, whether network shares were involved, and whether other endpoints show related activity.
Backups, least privilege, network segmentation, and a tested incident-response plan remain essential.
7. EDR in a SOC Environment
EDR is most effective when integrated into a broader security operations workflow.
A typical workflow looks like this:
<box border radius="lg" padding={3} gap={1} align="center">
<box background="surface-secondary" radius="md" padding={3} width="100%" align="center">
**Endpoint activity**
<text size="sm" color="secondary">Processes, files, registry and network events</text>
</box>
<icon name="arrow-down" size="lg" color="secondary" />
<box background="surface" border radius="md" padding={3} width="100%" align="center">
**EDR sensor and analytics**
<text size="sm" color="secondary">Telemetry collection, rules and behavioural analysis</text>
</box>
<icon name="arrow-down" size="lg" color="secondary" />
<box background="surface" border radius="md" padding={3} width="100%" align="center">
**Alert and incident creation**
<text size="sm" color="secondary">Evidence, severity and related events</text>
</box>
<icon name="arrow-down" size="lg" color="secondary" />
<box background="surface" border radius="md" padding={3} width="100%" align="center">
**SOC investigation**
<text size="sm" color="secondary">Validate, correlate, scope and classify</text>
</box>
<icon name="arrow-down" size="lg" color="secondary" />
<box background="surface" border radius="md" padding={3} width="100%" align="center">
**Response and recovery**
<text size="sm" color="secondary">Contain, eradicate, recover and improve detections</text>
</box>
</box>
In many environments, EDR alerts are also forwarded to a Security Information and Event Management (SIEM) platform. The SIEM can correlate endpoint detections with authentication logs, firewall events, cloud audit records, email security alerts, and other data sources.
For example, an EDR alert for suspicious execution may become more serious if the same user has an unusual sign-in, or if multiple endpoints communicate with the same suspicious destination.
A Security Orchestration, Automation and Response (SOAR) platform may then automate enrichment, ticket creation, notifications, or approved containment steps.
Automation should be designed with appropriate safeguards. Automatically isolating every endpoint that triggers a noisy detection can disrupt legitimate business activity.
8. EDR vs Antivirus vs SIEM vs XDR
These technologies complement one another, but they serve different purposes.
TechnologyPrimary purposeAntivirusDetects and blocks malware and other threats using supported signatures and detection methodsEDRProvides endpoint telemetry, behavioural detection, investigation, and response capabilitiesSIEMCollects and correlates security events from multiple sources for monitoring and investigationXDRCorrelates security signals across multiple domains, which may include endpoint, identity, email, and networkSOARAutomates and orchestrates security workflows and response actions
An organisation may use all these technologies together. The exact boundaries overlap because modern products increasingly combine multiple capabilities.
EDR does not replace a SIEM, identity security, network monitoring, vulnerability management, or sound security practices.
9. Limitations of EDR
EDR significantly improves endpoint visibility, but it is not a complete security solution.
Telemetry gaps: Disabled sensors, unsupported platforms, configuration issues, and retention limits may leave important activity unavailable.
False positives: Legitimate administration, software deployment, and development activity can resemble malicious behaviour.
False negatives: New or carefully designed attacks may evade existing detections or exploit gaps in monitoring.
Compromised privileges: An attacker with high privileges may attempt to interfere with endpoint protection or its supporting infrastructure.
Limited scope: Endpoint-focused telemetry may not fully explain cloud-control-plane activity, identity compromise, or network events occurring outside the monitored device.
Response risks: Automated remediation can interrupt business operations or remove evidence if it is not designed carefully.
To address these limitations, organisations should combine EDR with layered security controls, centralised logging, identity protection, network monitoring, secure configuration, and tested incident-response procedures.
10. Improving EDR Detection and Response
Security teams can improve EDR effectiveness through continuous monitoring and disciplined investigation.
Maintain sensor coverage: Confirm that critical endpoints are onboarded, reporting, and using supported configurations.
Tune detections: Reduce recurring false positives while preserving visibility into meaningful attack behaviour.
Correlate events: Combine process, file, network, identity, and security-configuration evidence.
Use threat hunting: Search for suspicious behaviours that have not triggered an alert.
Map detections to MITRE ATT&CK: Identify technique coverage and potential visibility gaps.
Test response workflows: Validate isolation, process termination, evidence collection, and recovery procedures.
Protect the management plane: Restrict administrative access to the EDR console and monitor changes to policies and permissions.
Measure operational performance: Track investigation time, containment time, false-positive rates, telemetry coverage, and detection gaps.
The objective is not simply to generate more alerts. It is to identify meaningful threats, reduce investigation time, and contain incidents with minimal unnecessary disruption.
Conclusion
EDR solutions help organisations detect and respond to cyberattacks by collecting endpoint telemetry, analysing behaviour, correlating related events, and supporting investigation and containment.
Their greatest value comes from connecting seemingly unrelated actions into a coherent picture of an attack. A suspicious script, a new registry entry, and an unusual outbound connection may each require context, but together they can reveal a potentially malicious sequence.
For SOC analysts, EDR is both a detection source and an investigation platform. Its effectiveness depends on sensor coverage, detection quality, integration with other security tools, and the ability to validate alerts and respond appropriately.
Further Reading
MITRE ATT&CK — Adversary tactics and techniques.
Microsoft Defender for Endpoint documentation — Endpoint protection, investigation, and response.
CISA — Cybersecurity guidance and incident-response resources.
NIST Cybersecurity Framework — Guidance for managing cybersecurity risk.