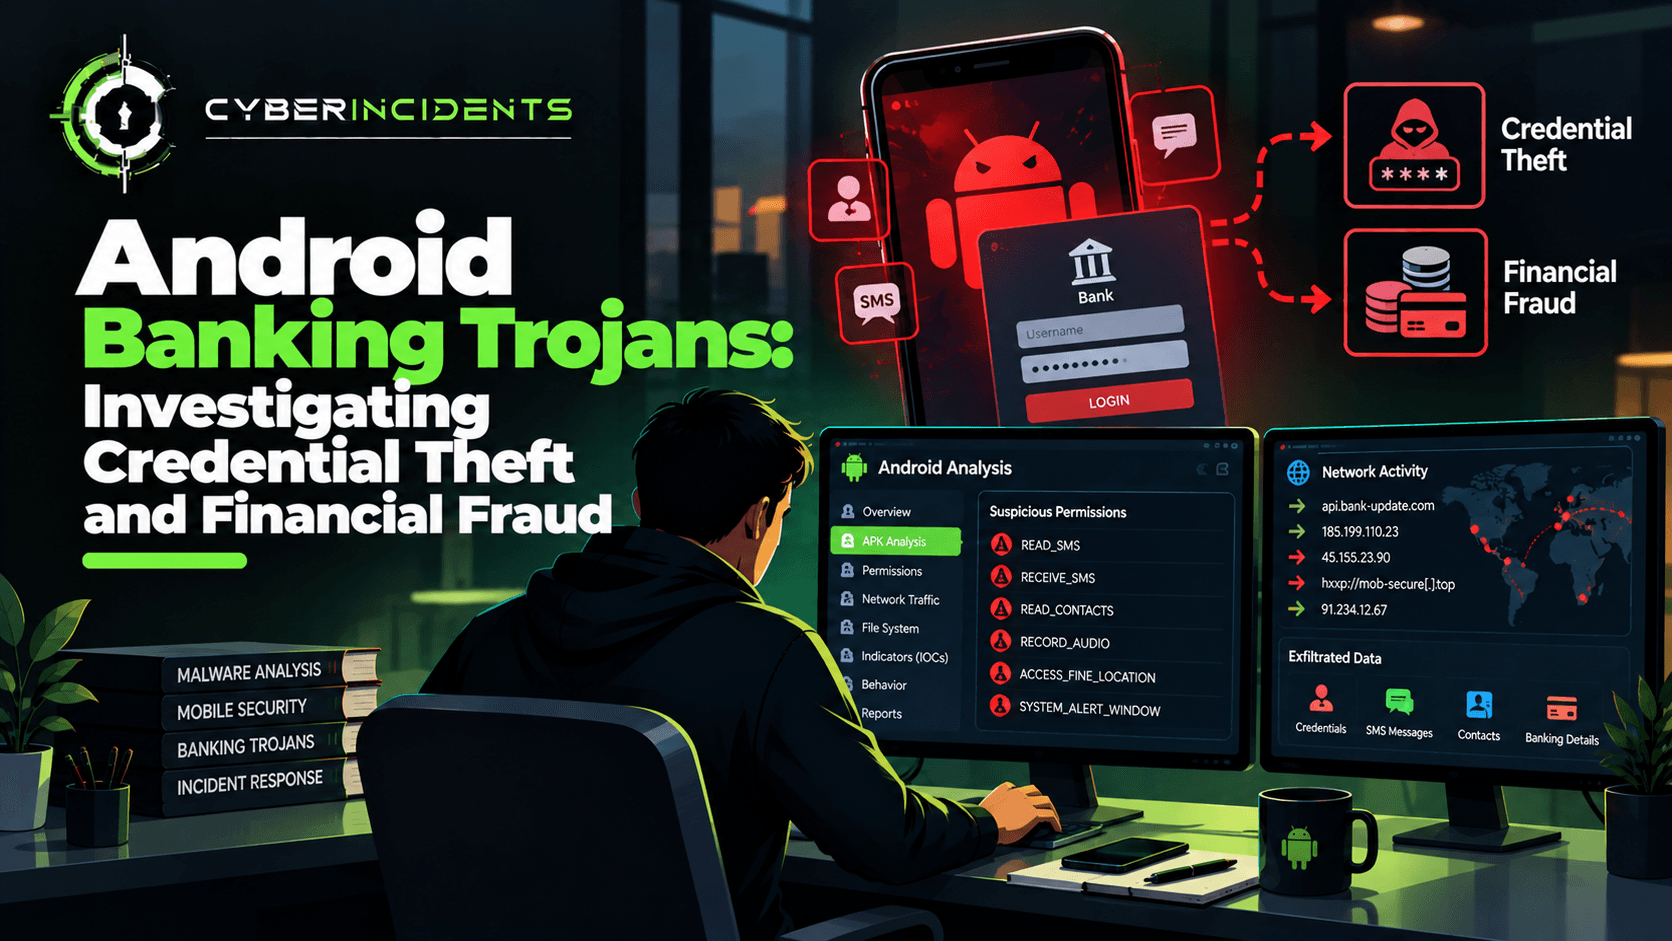
Android banking Trojans are malicious applications designed to steal banking credentials, intercept authentication information, manipulate user interactions, or facilitate unauthorised financial transactions. They may impersonate legitimate banking applications, abuse Android accessibility services, display fraudulent overlays, or exploit permissions granted by unsuspecting users.
Investigating these incidents requires analysts to correlate mobile device artefacts, application permissions, malware behaviour, network traffic, authentication logs, and banking transaction records. The goal is to determine how the device was compromised, what information may have been exposed, whether fraudulent transactions occurred, and which containment measures are necessary.
This article explores common Android banking Trojan techniques, a practical investigation workflow, forensic evidence sources, detection opportunities, and defensive measures for mobile users and financial institutions.
1. Introduction: When a Banking Application Becomes a Target
A bank's fraud monitoring team detects several suspicious transactions associated with a customer's account. The transactions occurred shortly after the customer installed an application claiming to provide a document-scanning service.
At approximately the same time, the customer's Android device generated unusual network activity. The application had requested accessibility permissions, and the customer reported seeing unexpected screens while using their banking application.
Investigators suspect that the installed application may have been involved in credential theft or transaction manipulation.
The investigation must establish:
Which application was installed and how it reached the device.
Whether the application exhibited malicious behaviour.
Whether credentials, authentication codes, or session information were exposed.
Whether the attacker gained access to the victim's banking account.
Whether fraudulent transactions were initiated or completed.
Which evidence connects the mobile device to the financial activity.
The challenge is that legitimate banking activity and malicious activity may occur within the same application session. Investigators must distinguish normal user actions from interactions that may have been influenced or performed by malware.
2. What Are Android Banking Trojans?
Android banking Trojans are a category of mobile malware that targets financial applications, payment services, cryptocurrency wallets, or other systems containing valuable authentication information.
Unlike malware that primarily damages a device, banking Trojans often aim to monetise access by stealing credentials, manipulating transactions, or enabling account takeover.
Common objectives include:
Capturing banking usernames and passwords.
Stealing one-time passwords (OTPs) or other authentication information.
Abusing accessibility services to observe or manipulate user interactions.
Displaying fake login screens over legitimate applications.
Reading notifications containing sensitive information.
Collecting device and application information.
Abusing remote-control capabilities to assist fraudulent activity.
Maintaining access to the device or communicating with attacker-controlled infrastructure.
Not every banking Trojan uses all these techniques. Capabilities vary by malware family, Android version, permissions, device configuration, and the protections implemented by the targeted banking application.
3. Common Attack Techniques
3.1 Fake Applications and Malicious Installation
An infection may begin when a user installs a malicious application disguised as a legitimate utility, security tool, document viewer, delivery application, or banking-related service.
Possible delivery channels include deceptive websites, malicious advertisements, phishing messages, third-party application repositories, or social engineering that persuades users to install an application manually.
Investigators should determine:
The application's package name and version.
Its installation source, where recorded.
Its signing certificate and cryptographic hashes.
Its requested and granted permissions.
Its installation and first-observed timestamps.
Whether the application was associated with a known legitimate publisher.
A familiar application name or icon is not proof of legitimacy. Package identity, signing information, application provenance, and behaviour provide stronger investigative context.
3.2 Overlay Attacks and Fake Login Screens
Some banking Trojans use overlay techniques to display a fraudulent interface that resembles a legitimate banking application.
A victim may enter credentials into the fake interface believing they are interacting with their bank. The malicious application may capture the entered information or use it to facilitate subsequent account compromise.
Investigators should examine:
Unexpected overlay-related permissions or behaviours.
Application activity occurring when the banking app is opened.
Accessibility events and window-related telemetry, where available.
Evidence of a suspicious application appearing above a financial application.
Authentication events that follow the suspected interaction.
An overlay capability does not establish that credentials were captured. The investigator needs supporting evidence from application behaviour, device telemetry, malware analysis, or subsequent account activity.
3.3 Abuse of Android Accessibility Services
Android accessibility services are designed to support users who need assistance interacting with their devices. Depending on the service and Android version, these capabilities can expose information about interface elements or allow certain interactions with applications.
Malicious applications may attempt to persuade users to enable accessibility services by presenting misleading explanations or repeated prompts.
When abused, these capabilities may support:
Observing application interface content.
Automating user-interface interactions.
Interfering with security prompts.
Navigating through application screens.
Facilitating unauthorised actions within accessible interfaces.
Investigators should identify which application registered the service, whether the user enabled it, what behaviour the service performed, and whether the activity aligns with the application's legitimate purpose.
Accessibility permission alone is not evidence of malware. Many legitimate applications require accessibility functionality.
3.4 OTP and Notification Interception
Some banking Trojans attempt to obtain authentication information delivered through notifications or other communication channels.
Depending on the malware's capabilities and the device configuration, this may involve notification access, SMS-related permissions, accessibility abuse, or other methods of collecting authentication information.
Investigators should examine:
Notification-access settings.
SMS permissions and relevant application behaviour.
Available message or notification artefacts.
Authentication challenges recorded by the bank.
Changes to authentication methods or trusted devices.
Timing between suspected credential exposure and account activity.
An OTP-related event does not automatically mean that the Trojan intercepted the code. Investigators should establish whether the application could access the information and whether there is evidence linking it to the subsequent authentication.
3.5 Remote Interaction and Transaction Manipulation
Certain malware families provide capabilities that allow an attacker to observe or influence device activity remotely. Combined with credential theft or accessibility abuse, this may assist fraudulent transactions.
Possible indicators include:
Unexpected foreground application changes.
Accessibility-driven interactions.
Unusual screen activity.
Remote-control or device-management components unrelated to the application's purpose.
Banking transactions occurring during a suspicious device session.
Remote interaction capability should be distinguished from proof that an attacker personally operated the device. Device telemetry may reveal suspicious activity without establishing exactly who initiated each interaction.
4. Reconstructing the Attack Chain
A successful investigation connects mobile device activity to authentication events and financial outcomes.
Consider the following hypothetical incident timeline:
Time (UTC)EvidenceInvestigative significance08:42A new application is installedEstablishes a possible initial entry point08:49The application receives accessibility accessIdentifies a potentially sensitive permission change09:03The banking application is openedEstablishes relevant user activity09:04Suspicious application or accessibility activity is observedMay indicate interference with the banking session09:07A new banking authentication event occursRequires validation against the customer's normal activity09:12A new beneficiary is addedMay indicate account manipulation09:16An unusual transfer is initiatedEstablishes a potential financial impact09:21The bank flags the transactionTriggers the investigation
This timeline is illustrative and does not describe a confirmed real-world incident.
The sequence raises suspicion, but it does not independently prove that the installed application stole credentials or initiated the transfer. Investigators should correlate device evidence with banking records, authentication telemetry, and the bank's transaction assessment.
5. Mobile Forensic Evidence Sources
Android investigations can be challenging because artefact availability depends on Android version, application design, device security controls, encryption, and the acquisition method.
5.1 Installed Application Information
Application metadata can help identify suspicious software.
Investigators should collect, where available:
Package name.
Application version.
APK or split APK hashes.
Signing certificate information.
Installation source and timestamps.
Requested and granted permissions.
Application manifest information.
Associated network destinations.
Relevant application and system logs.
An APK hash can support comparison with known samples, while signing information can help establish whether an application was signed by an expected publisher. Neither should be interpreted without appropriate reference data.
5.2 Android Permission and System Artefacts
Review relevant permission grants, accessibility settings, notification access, device administrator settings, and other security-sensitive configuration changes.
The precise location and availability of these records vary by Android release and acquisition method. Investigators should avoid assuming that every permission change is preserved in a directly accessible historical log.
Where possible, correlate current settings with EDR or mobile threat defence telemetry, device management records, application installation evidence, and system logs.
5.3 Application Data and Logs
Application-private storage may contain databases, configuration files, cached information, or logs relevant to the investigation.
Access to this information may require an authorised forensic acquisition method. Android application sandboxing and device encryption can prevent direct access to some artefacts.
Investigators should preserve evidence using approved procedures and avoid modifying the original device unnecessarily.
5.4 Network Evidence
Network records may reveal communication between a suspicious application and external infrastructure.
Potential sources include:
DNS logs.
Firewall and proxy records.
VPN telemetry.
Mobile threat defence alerts.
Network connection metadata.
Relevant application or system logs.
Server-side records, where available.
Investigate destination reputation, timing, connection patterns, and the relationship between network activity and suspected credential exposure.
Encrypted traffic usually limits the ability to determine the exact content transmitted. A connection to a suspicious destination does not, by itself, prove that banking credentials were uploaded.
5.5 Banking and Identity Records
Financial institutions may provide some of the most valuable evidence for determining whether the attack caused account compromise or financial loss.
Relevant records can include:
Successful and failed authentication attempts.
Device registration and trusted-device changes.
MFA challenges and outcomes.
Password or recovery-method changes.
Beneficiary creation and modification.
Transaction initiation and completion records.
Transaction risk scores and fraud alerts.
Relevant customer reports and confirmation records.
These records help establish the financial impact, even when the mobile device does not retain enough evidence to reconstruct every action.
6. SOC Investigation: A Step-by-Step Workflow
Step 1: Validate the Alert
Determine whether the alert originates from mobile threat defence, endpoint telemetry, banking fraud monitoring, an identity provider, or a customer report.
Collect the device identifier, user or account reference, application details, timestamps, and detection rationale.
Separate confirmed malware detections from heuristic alerts or suspicious application behaviour.
Step 2: Identify the Suspected Application
Examine the application's package name, version, signing certificate, installation source, permissions, and behaviour.
Compare the application against trusted publisher information and reputable malware intelligence sources.
Do not label an application malicious solely because it requests a sensitive permission. Validate whether the permission is necessary for its stated purpose and whether its behaviour supports the suspected attack.
Step 3: Examine Sensitive Permissions
Investigate accessibility access, notification access, SMS permissions, and other capabilities that may expose sensitive information.
Establish when the permissions were granted, which application received them, and whether suspicious behaviour followed.
Where historical permission-change evidence is unavailable, document that limitation rather than assuming when the permission was enabled.
Step 4: Correlate Authentication Activity
Review banking and identity-provider logs for unusual authentication events following the suspected infection.
Investigate unfamiliar devices, unexpected locations, changes in authentication patterns, new trusted devices, and unusual MFA activity.
Consider legitimate explanations such as travel, VPN use, device replacement, or banking application updates.
Step 5: Investigate Financial Activity
Determine whether new beneficiaries, payment instructions, account settings, or transactions changed during the incident window.
Establish whether transactions were attempted, authorised, completed, reversed, or blocked.
Where available, correlate transaction timestamps with authentication events and device telemetry. Financial activity must be evaluated using the bank's records rather than inferred solely from suspicious device behaviour.
Step 6: Assess the Impact
Determine which of the following conclusions are supported:
A suspicious application was installed.
The device exhibited behaviour consistent with credential theft.
Authentication information may have been exposed.
Unauthorised account access was confirmed.
Fraudulent transactions were attempted.
Financial loss or data exposure was confirmed.
These are different findings. A report should state clearly which are confirmed, which are inferred, and which remain unresolved.
Step 7: Contain and Recover
Coordinate with the device owner, incident response team, and financial institution.
Depending on the evidence, actions may include isolating the device, removing malicious applications through an approved process, revoking sessions, changing exposed credentials from a trusted device, resetting authentication methods, and blocking fraudulent transactions.
If financial fraud is suspected, contact the bank promptly through a verified channel. Preserve the device and relevant evidence before performing actions that could destroy useful artefacts, unless immediate action is required to prevent further harm.
7. Detection Engineering and Correlation
Detection 1: Suspicious Application with Sensitive Permissions
Raise an alert when an application with limited or unclear business justification receives sensitive permissions and exhibits suspicious behaviour.
Enrich the detection with application provenance, signing information, known malware intelligence, and permission history.
Detection 2: Mobile Malware Alert Followed by Unusual Banking Activity
Correlate mobile threat defence alerts with authentication anomalies and banking fraud signals.
For example, a confirmed infostealer detection followed shortly by unfamiliar account access and a new beneficiary should receive greater investigative priority than any one event in isolation.
Detection 3: New Device or Authentication Context
Monitor new device registrations, unexpected authentication patterns, and unusual changes to recovery or authentication methods.
A new device is not automatically malicious. Detection quality improves when identity history, device reputation, and transaction context are included.
Detection 4: Accessibility Abuse Indicators
Where supported by mobile security tooling, monitor applications that unexpectedly request or abuse accessibility services, especially when combined with overlay behaviour or suspicious network activity.
Do not rely on the permission itself as a malware verdict.
Detection 5: Suspicious Transaction Sequence
Financial institutions can correlate authentication anomalies, beneficiary changes, device-risk signals, and unusual transaction behaviour.
Risk-based controls may trigger additional verification, transaction delays, or manual review according to the institution's fraud policies.
8. MITRE ATT&CK Mapping
The following techniques may be relevant when supported by evidence. Verify the current descriptions in the MITRE ATT&CK Mobile knowledge base before final classification.
TechniqueATT&CK IDInvestigative relevanceInput CaptureT1417Evidence supports collection of user input on a mobile deviceCapture Clipboard DataT1412Evidence supports collection of clipboard contentsAccess Sensitive Data in DeviceT1636Evidence supports access to sensitive information stored on the deviceSteal Application Access TokenT1528Evidence supports theft of an application access tokenAbuse Accessibility FeaturesT1453Evidence supports malicious abuse of Android accessibility capabilitiesPhishingT1660Evidence supports phishing used to obtain information or facilitate compromise
ATT&CK mappings describe observed behaviours, not proof of financial fraud. For example, the presence of an accessibility service does not automatically establish abuse, and a suspicious sign-in does not by itself prove token theft.
Reference: https://attack.mitre.org/techniques/mobile/
9. Prevention and Hardening
Install applications from trusted sources. Use official application stores and verify the publisher. Treat unexpected installation links and requests to sideload applications with caution.
Review sensitive permissions. Regularly examine accessibility, notification, SMS, and device-administration permissions. Revoke access that is unnecessary or cannot be justified.
Keep Android updated. Install supported security updates and update banking applications through trusted channels.
Use strong authentication. Enable the bank's supported MFA and transaction verification features. Remember that MFA does not prevent every token-theft or session-abuse scenario.
Protect devices against malware. Use reputable mobile security controls where appropriate, and investigate warnings about suspicious applications or credential-stealing behaviour.
Apply banking risk controls. Financial institutions should use device-risk signals, behavioural analytics, transaction monitoring, and additional verification for high-risk actions.
Secure credentials and sessions. Avoid entering banking credentials into unexpected screens. If compromise is suspected, revoke sessions and reset credentials through verified channels.
Preserve evidence during response. Avoid factory-resetting a suspected device before considering forensic requirements, unless immediate containment or personal safety makes it necessary.
Educate users. Explain how social engineering, fake applications, and permission abuse can facilitate fraud. Encourage customers to report suspicious transactions immediately.
Conclusion
Android banking Trojans can turn a compromised mobile device into a pathway for credential theft, account takeover, and financial fraud. Their capabilities vary, but common investigative themes include suspicious application installation, sensitive permission abuse, authentication anomalies, and unauthorised financial activity.
A strong investigation correlates mobile application evidence, device telemetry, identity logs, network records, and banking transactions. Analysts must distinguish potential credential exposure from confirmed account compromise and confirmed financial loss.
For SOC teams and digital forensic investigators, the objective is to reconstruct the attack chain, establish the scope of exposure, preserve relevant evidence, and coordinate containment before further transactions occur.
Further Reading